
UK Cybersecurity Market Size and Share
Market Overview
| Study Period | 2020 - 2031 |
|---|---|
| Forecast Data Period | 2026 - 2031 |
| Base Year Market Size (2025) | USD 14.77 Billion |
| Market Size (2026) | USD 16.27 Billion |
| Market Size (2031) | USD 25.13 Billion |
| Growth Rate (2026 - 2031) | 9.09 % |
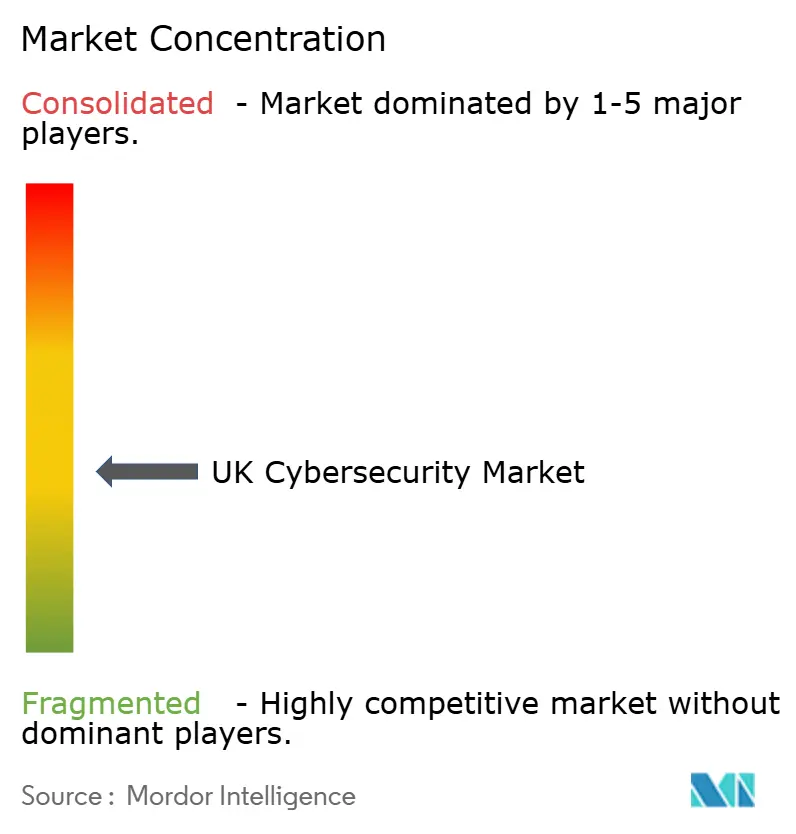
| Market Concentration | Medium |
Major Players *Disclaimer: Major Players sorted in no particular order Image ? 黑料不打烊. Reuse requires attribution under CC BY 4.0. | |
UK Cybersecurity Market Analysis by 黑料不打烊
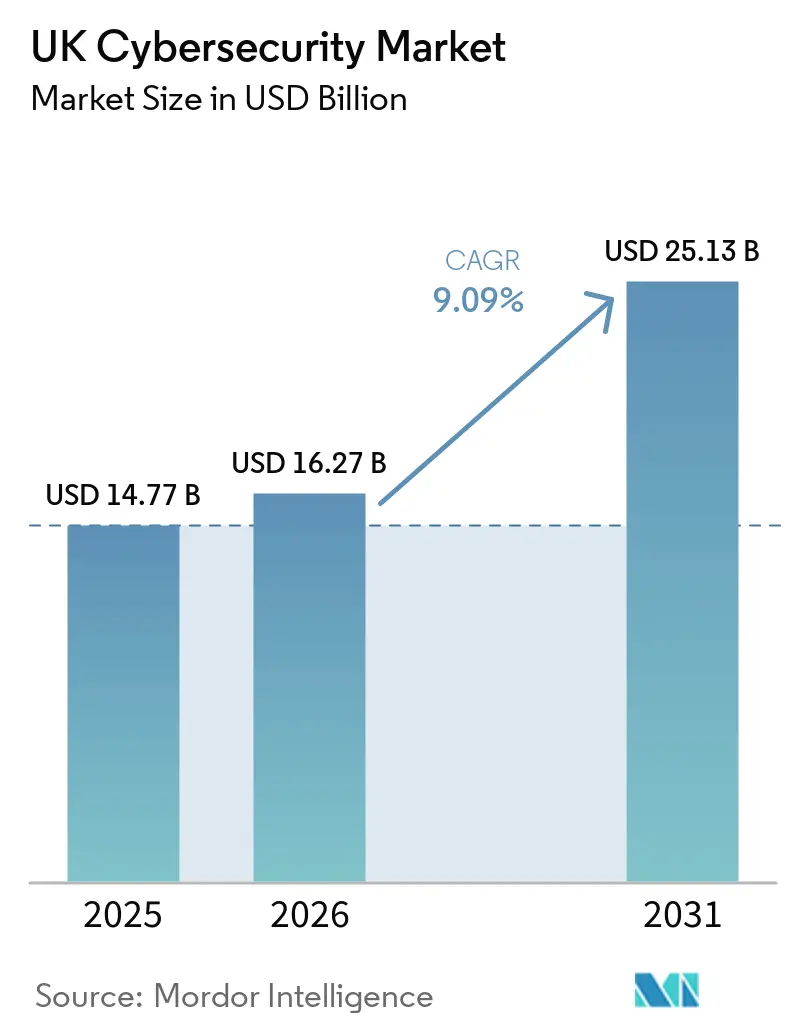
The UK cybersecurity market size was valued at USD 14.77 billion in 2025 and estimated to grow from USD 16.27 billion in 2026 to USD 25.13 billion by 2031, reflecting a 9.09% CAGR during the forecast period (2026-2031). This market size expansion is driven by the rapid escalation of ransomware attacks on critical infrastructure, mandatory zero-trust requirements in public procurement, and stringent compliance milestones under the Telecommunications Security Act and the Digital Operational Resilience Act. Spending momentum is strongest among enterprises migrating to cloud-native security service edge frameworks, while managed detection and response deals flourish as boards accept that 24 x 7 threat monitoring is now a baseline requirement rather than a premium add-on. Competitive pressure from both multinational suites and highly specialized local providers fuels continuous product innovation, particularly around artificial-intelligence analytics that shorten the dwell time of advanced persistent threats. Procurement teams also favor platforms that consolidate audit trails across multiple regulations, which encourages supplier consolidation and multi-year service contracts that lock in predictable cost structures.
Key Report Takeaways
- By offering solutions with a 62.73% revenue share in the UK cybersecurity market in 2025, while services advance at a 12.22% CAGR through 2031.
- By deployment mode, cloud captured 63.84% share of the UK cybersecurity market size in 2025 and is expanding at a 12.32% CAGR through 2031.
- By end-user industry, banking, financial services, and insurance (BFSI) commanded 29.73% of the UK cybersecurity market share in 2025, whereas the healthcare and life sciences industry is forecast to grow at a 13.67% CAGR to 2031.
- By organization size, large enterprises accounted for 61.74% of 2025 spending, while small and medium enterprises are accelerating at a 12.46% CAGR through 2031.
Note: Market size and forecast figures in this report are generated using 黑料不打烊’s proprietary estimation framework, updated with the latest available data and insights as of January 2026.
UK Cybersecurity Market Trends and Insights
Drivers Impact Analysis*
| Driver | (~) % Impact on CAGR Forecast | Geographic Relevance | Impact Timeline |
|---|---|---|---|
| Escalating Digitalisation and Hybrid-Work Attack Surface | +2.3% | National, concentrated in London, Manchester, Edinburgh financial and tech hubs | Medium term (2-4 years) |
| Surge in Ransomware and Nation-State Threats | +2.1% | National, acute in healthcare trusts, local government, energy utilities | Short term (≤ 2 years) |
| Growing UK Compliance Mandates (Telecom Security Act, DORA) | +1.9% | National, with heightened enforcement in BFSI and telecommunications sectors | Medium term (2-4 years) |
| Rapid Adoption of AI-Driven Security Analytics | +1.7% | National, early gains in large enterprises and managed service providers | Long term (≥ 4 years) |
| Government Zero-Trust Procurement Requirements | +1.4% | Public sector, cascading to defense contractors and critical national infrastructure suppliers | Medium term (2-4 years) |
| Cyber-Insurance Underwriting Pressures Shaping Controls | +1.2% | National, most pronounced in SME segment and high-risk verticals | Short term (≤ 2 years) |
| Source: 黑料不打烊 | |||
Escalating Digitalization and Hybrid-Work Attack Surface
Hybrid work dismantled the traditional perimeter, so organizations now defend thousands of endpoints that sit on domestic broadband with inconsistent patch regimes. National guidance urges secure access service edge rollouts that blend firewall, secure web gateway, and zero-trust network access in a single cloud stack, enabling uniform policies regardless of user location. Regulated firms must also maintain continuous authentication and micro-segmentation, a requirement that effectively pushes cloud-native adoption across finance and technology hubs. Seventy-three percent of large employers intend to keep flexible work patterns, which cements identity-centric security as a long-term necessity. As a result, cloud deployments outpace on-premise alternatives, and vendors heavily promote policy engines that span both remote and campus networks.
Surge in Ransomware and Nation-State Threats
The National Cyber Security Center recorded a 68% year-on-year jump in ransomware incidents during 2025, linking the spike to ransomware-as-a-service kits that allow entry-level affiliates to execute sophisticated attacks.[1]National Cyber Security Centre, “Annual Review 2025,” ncsc.gov.uk Healthcare systems experienced prolonged outages, while energy utilities faced supply chain intrusions traced to Russian and Iranian groups. A government survey found that 32% of businesses experienced breaches in 2025, with remediation costs averaging GBP 15,300 (USD 20,534.97). This heightened threat environment is driving growth in the UK cybersecurity market as enterprises increase investments in advanced threat detection, incident response, endpoint protection, cloud security, and security operations capabilities. Organizations are also prioritizing managed detection and response contracts that provide 24/7 coverage, faster containment, and direct escalation to incident response teams, as ransomware and nation-state activity continue to expose operational, financial, and regulatory risks.
Growing UK Compliance Mandates (Telecom Security Act, DORA)
Full enforcement of the Telecommunications Security Act from January 2025 obliges network operators to excise high-risk vendors and adopt continuous vulnerability scanning and encrypted signaling. Parallel preparations for the Digital Operational Resilience Act require annual resilience testing, third-party risk reviews, and near-real-time incident notification in financial services. Banks earmarked more than GBP 1.2 billion (USD 1.61 billion) for compliance-driven security upgrades during 2025, reinforcing demand for platforms that automate evidence gathering across frameworks. Vendors that fuse risk management, penetration testing, and reporting functionality therefore enjoy a sizeable procurement advantage.
Rapid Adoption of AI-Driven Security Analytics
Artificial-intelligence analytics increasingly supplement signature-based controls by profiling normal behavior and flagging anomalies that signal lateral movement or data exfiltration. Darktrace reported a significant rise in UK customers using autonomous response modules that can quarantine suspicious activity without human approval. These gains underline a market appetite for tools that compress detection-to-containment cycles from hours to minutes. Yet, adversarial inputs can still poison machine-learning models, so the UK AI Safety Institute continues to develop assurance standards. As best practice matures, enterprises broaden pilot projects into enterprise-wide rollouts, ensuring AI analytics remain a solid contributor to long-term growth.
Restraints Impact Analysis*
| Restraint | (~) % Impact on CAGR Forecast | Geographic Relevance | Impact Timeline |
|---|---|---|---|
| Acute Cyber-Skills Deficit | -1.8% | National, most severe in regions outside London and Southeast | Long term (≥ 4 years) |
| High Total Cost of Ownership for Advanced Platforms | -1.3% | National, concentrated in SME and mid-market segments | Medium term (2-4 years) |
| Legacy OT and Critical-Infrastructure Systems Hard to Secure | -0.9% | Energy, utilities, oil and gas, manufacturing sectors | Long term (≥ 4 years) |
| SME Under-Investment Given Unclear ROI | -0.7% | National, acute in retail, hospitality, transport, logistics | Short term (≤ 2 years) |
| Source: 黑料不打烊 | |||
Acute Cyber-Skills Deficit
Government estimates indicated a significant number of cybersecurity vacancies nationwide in 2025, while senior cloud security engineers in London commanded high median salaries. This acute shortage of skilled professionals continues to challenge the growth of cybersecurity in the United Kingdom by increasing labor costs, extending implementation timelines, and limiting the ability of organizations to deploy advanced security solutions at scale. Enterprises often struggle to recruit and retain specialists with expertise in cloud security, threat detection, incident response, and regulatory compliance, which slows digital transformation initiatives and weakens overall security maturity. The skills gap also places pressure on internal teams, increases operational risk, and makes it difficult for organizations to respond quickly to evolving cyber threats. As a result, many enterprises are outsourcing security operations to specialist providers to maintain resilience and continuity. Apprenticeship schemes and university investments may ease shortages in the medium term, but managed services remain the primary stopgap, reinforcing their double-digit growth trajectory.
High Total Cost Of Ownership For Advanced Platforms
Licenses for extended detection and response or identity governance suites often exceeded GBP 50,000 (USD 67,107.75) annually for mid-sized businesses in 2025, while integration projects added another 30-50% in service fees. These costs created a significant restraint on the growth of cybersecurity adoption in the United Kingdom, particularly among small and medium enterprises, which comprise 99% of UK companies. Many of these businesses found it difficult to justify such expenditures because the return on investment depended largely on avoiding potential breach losses rather than generating immediate operational gains. The Federation of Small Businesses reported that 41% of its members cited budget constraints as the main barrier to adopting advanced controls. High upfront licensing costs, additional implementation expenses, and ongoing maintenance requirements also slowed the deployment of more sophisticated cybersecurity platforms across resource-constrained organizations.[2]Federation of Small Businesses, “Small Business Cyber Security Report 2025,” fsb.org.uk Although vendors responded with usage-based pricing, overall affordability continued to limit broader adoption and remained a key challenge for cybersecurity market growth in the United Kingdom.
*Our forecasts treat driver/restraint impacts as directional, not additive. The impact forecasts reflect baseline growth, mix effects, and variable interactions.
Segment Analysis
By Offering: Services Command Spending As In-House Skills Erode
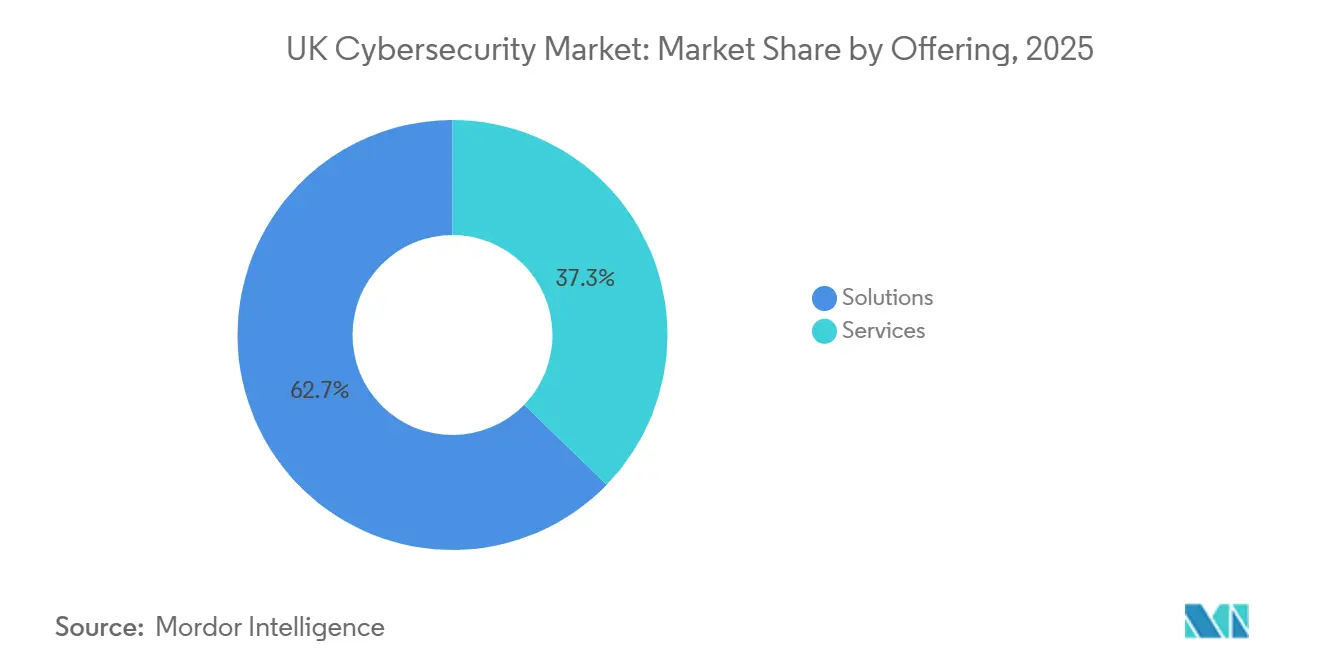
Solutions dominated the UK cybersecurity market in 2025, accounting for 62.73% of total market revenue. This significant share reflected the fundamental need for organizations across the UK to deploy robust security technologies, including network security appliances, endpoint protection platforms, firewalls, encryption tools, identity and access management systems, and SIEM solutions. The dominance of the solutions segment stemmed from businesses’ critical need to establish baseline security infrastructure before adopting complementary services. This need increased as organizations faced more sophisticated cyber threats and had to comply with stringent regulatory frameworks, such as GDPR and the UK's National Cyber Security Strategy. Large enterprises and public sector organizations typically led solutions procurement, investing heavily in comprehensive security technology stacks to protect their extensive digital assets and customer data.
Furthermore, the services segment is projected to register a compound annual growth rate (CAGR) of 12.22% through 2031, making it the fastest-growing offering category in the UK cybersecurity market. Several factors drive this accelerated growth, including the acute shortage of in-house cybersecurity expertise across UK organizations, the increasing complexity of security operations requiring specialized knowledge, and the rising adoption of managed security services that enable businesses to outsource security monitoring and incident response. The services segment includes consulting, implementation, managed security services, incident response, penetration testing, vulnerability assessments, and security training programs. These services are becoming increasingly essential as organizations seek to maximize the effectiveness of their security technology investments and maintain continuous protection against evolving cyber threats. The shift toward subscription-based and as-a-service models further supports this growth by making advanced security capabilities more accessible to small and medium-sized enterprises across the UK.


By Deployment Mode: Cloud Solutions Dominate As Perimeter Dissolves
Cloud deployment captured 63.84% of the UK cybersecurity market size in 2025 and is projected to grow at a CAGR of 12.32% through 2031, while on-premises deployments are expected to expand at mid-single-digit rates. Remote and hybrid workforces require identity-centric architectures, so organizations adopt security service edge platforms that enforce consistent policies across any location. Government and financial regulators endorse multi-cloud strategies paired with centralized identity federation, which further validates vendor roadmaps built around cloud-first controls. Enterprises note that activating cloud protection can take days, whereas procurement, racking, and maintenance cycles slow on-premises platforms. Even industries with strict data localization rules embrace hybrid designs that keep sensitive records onsite but shift analytics to elastic cloud nodes.
On-premises estates persist in segments that run legacy operational technology, such as manufacturing, energy, and utilities. Air-gapped programmable logic controllers cannot interface with external platforms, so asset owners deploy intermediary sensors and network taps to gain telemetry. Vendors blend these deployments with cloud-hosted management consoles, which illustrates the broader trend toward flexible consumption models. However, migration introduces misconfiguration risks, and cloud security posture management is now bundled into most enterprise contracts to check compliance against Center for Internet Security benchmarks automatically.
By End-User Industry: Healthcare and Life Sciences Growth Surges as BFSI Remains Core
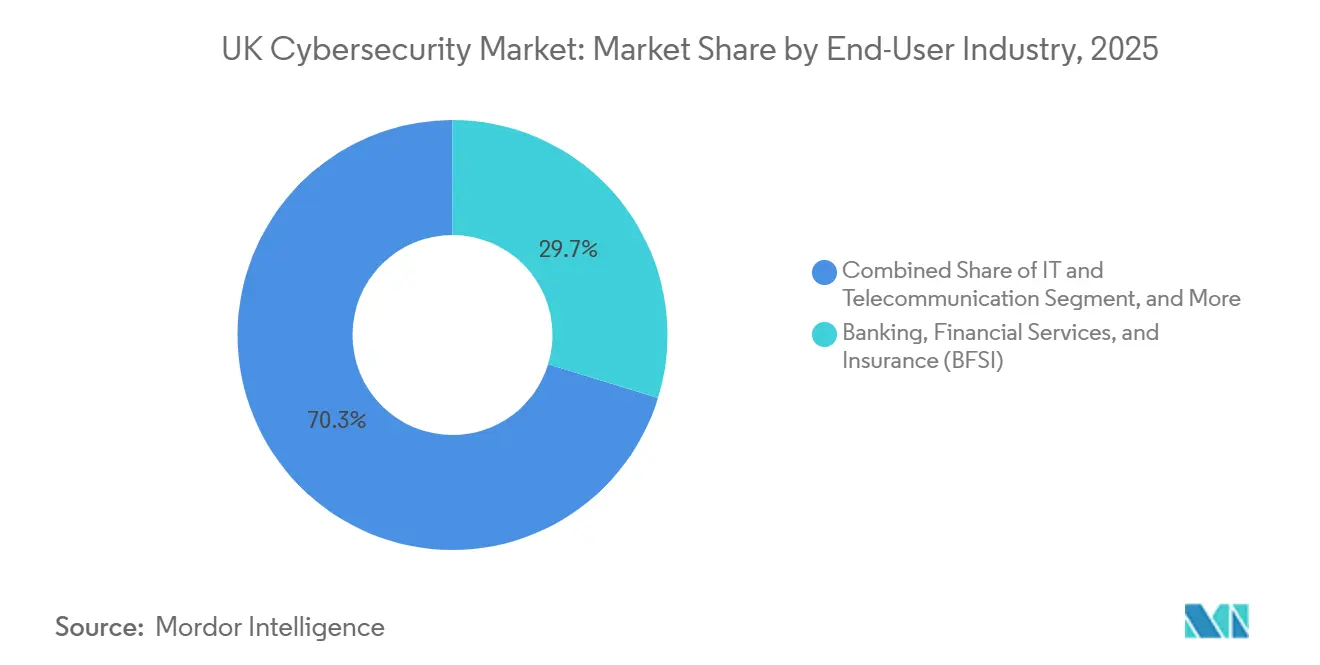
Banking, financial services, and insurance (BFSI) retained 29.73% of the UK cybersecurity market share in 2025, a position underpinned by continuous regulatory scrutiny from the Financial Conduct Authority and the Prudential Regulation Authority.[3] Budgets cover zero-trust migration for trading platforms, continuous monitoring of third-party vendors, and automated reporting for operational resilience tests. Healthcare and life sciences record the swiftest expansion with a 13.67% CAGR through 2031. Ransomware attacks on hospital trusts in 2025 triggered delays in elective surgery and prompted a government-backed uplift program to fund endpoint detection, network segmentation, and encrypted backups. Moreover, electronic health record modernization goes hand in hand with enhanced identity management to protect sensitive patient data.
Government ministries and local councils also increase spending to satisfy zero-trust mandates that now form mandatory contractual language for all departments. Telecommunications operators invest heavily to swap high-risk 5G components and harden signaling. Retail and e-commerce entities deploy fraud detection and tokenization to stem an 18% rise in card-not-present transactions. Manufacturing and industrial sectors focus on network segmentation within supervisory control networks, while energy utilities adopt anomaly-detection sensors to monitor power-generation turbines. Despite varied priorities, every vertical now views cybersecurity as a board-level operational requirement rather than an IT line item.

By Organization Size: SME Adoption Gains Momentum Under Insurance Pressure
Large enterprises accounted for 61.74% of 2025 spend, supported by in-house security engineering staff and multi-layered defenses that cover endpoints, networks, and cloud workloads. Growth in this tier is steady but incremental, given that many large organizations already operate mature security programs. Small and medium enterprises, by contrast, log a 12.46% CAGR, catalyzed by cyber-insurance underwriters that refuse cover unless buyers implement multi-factor authentication, maintain up-to-date software, and store offline backups. Insurers leverage actuarial claims to adjust pricing in real time, so SMEs quickly realize that even a modest investment in baseline controls can cut premiums by tangible percentages.
The UK cybersecurity market size for SMEs remains smaller in absolute terms, yet the addressable headcount of 5.5 million businesses makes the collective opportunity substantial. Vendors tailor bundles that fold endpoint, email, and web protection into a single agent, add managed detection oversight, and expose simplified dashboards suitable for non-specialists. Consumption-based packages resonate because SMEs can scale up during peak trading seasons and scale down afterward, flattening cost curves. As compliance pressures, insurance audits, and customer expectations converge, SME adoption deepens, closing the maturity gap versus large enterprises.
Geography Analysis
London and the Southeast dominated UK cybersecurity spending, accounting for a considerable share of national spend in 2025. The capital hosts a dense cluster of financial institutions, global law firms, and technology unicorns, each operating multi-cloud estates and facing stringent regulatory requirements. As a result, suppliers concentrate sales teams and demonstration centers within the M25 corridor. Scotland ranked second, supported by Edinburgh’s finance quarter and Glasgow’s maturing tech scene, which secured resources through the Scottish Government’s Cyber Resilience Strategy. The strategy funded security upgrades for SMEs and university laboratories. Regional managed service providers addressed skills gaps by co-locating operations centers near universities to access graduate talent pools.
The Midlands and Northern England showed moderate, but accelerating demand as manufacturing and logistics hubs digitized supply chains. In these regions, operational technology security drove purchases of anomaly-detection sensors and network-segmentation equipment, reflecting threats from nation-state actors probing industrial control systems. Wales and Northern Ireland remained smaller in absolute terms. However, government grants encouraged local councils and hospitals to migrate email, productivity software, and security controls to sovereign cloud platforms. Devolved cybersecurity strategies incentivized managed service providers to open satellite offices, ensuring on-the-ground incident response without lengthy travel.
Cross-border regulatory alignment further shaped the landscape. Post-Brexit, UK regulators mirrored the European Union’s Digital Operational Resilience Act to facilitate trade in financial services, prompting multinationals to demand tools that complied with both regulatory frameworks. Participation in Five Eyes intelligence networks provided early warnings of zero-day exploits, influencing vendor patch management timelines. In addition, joint exercises under NATO’s Cooperative Cyber Defense Center enhanced military and civilian readiness, resulting in the procurement of devices hardened to Common Evaluation Assurance Level benchmarks.
Regulatory Landscape
The UK cybersecurity framework is tightening expectations for public services, critical national infrastructure (CNI), and key digital suppliers through a mix of policy, sector regulation, and technical authority guidance. In January 2026, the UK Government published the Government Cyber Action Plan, led via the Government Cyber Unit, with GBP 210 million (USD 283.63 million) allocated to strengthen baseline controls across public sector organizations and raise resilience requirements in service delivery and procurement.
A parallel legislative track is also reshaping statutory obligations for operators and suppliers. The Cyber Security and Resilience (Network and Information Systems) Bill (2024-26) is progressing to refresh the 2018 NIS Regulations and broaden the scope of regulated entities, including data centres and other systemically important digital infrastructure. The National Cyber Security Centre (NCSC) continues to act as the technical authority for incident management and guidance, while sector competent authorities enforce compliance within their regulated domains, pushing demand for audit-ready security controls and third-party risk management tooling.
Value Chain Analysis
The UK cybersecurity value chain begins with solution and platform providers covering endpoint, network, cloud, IAM, and integrated risk management. Systems integrators, consultancies, and managed security service providers then support deployment and operations, including 24x7 monitoring, threat hunting, and incident response. Buyers are concentrated in BFSI, government/public sector, telecom, healthcare, and CNI operators, where procurement often bundles products with professional services for rollout, compliance mapping, and operational resilience testing.
Downstream delivery and supplier selection are also shaped by security assurance and procurement expectations. Government-led initiatives and policy direction emphasize supply-chain security, including use of Cyber Essentials for suppliers and tighter obligations for CNI under evolving NIS-related regulation. That pull extends to assessment bodies, certification, and continuous monitoring services, which in turn favors providers able to integrate controls across cloud and on-premises estates and produce evidence packages aligned to sector regulators and NCSC-informed best practices.
Competitive Landscape
The market is moderately fragmented, with the five largest vendors (Darktrace, Sophos, NCC Group, BAE Systems Digital Intelligence, and BT Security) holding a significant share in 2025. Darktrace capitalizes on machine-learning analytics that automatically quarantine anomalous behavior, winning contracts in sectors pressed by the cyber-skills shortage. Sophos differentiates through a global network of security operations centers that deliver managed detection and response aligned to mid-market price points. NCC Group leverages its deep penetration-testing roots to advise banks and telecom operators on their obligations under the Telecommunications Security Act and DORA.
Second-tier specialists, including Bridewell Consulting, Integrity360, and Quorum Cyber, capture niches by marrying domain knowledge with flexible commercial models.[4]Quorum Cyber, “Quorum Cyber’s 2026 Global Cyber Risk Mid-Year Review”, www.quorumcyber.com Bridewell helps healthcare trusts comply with National Health Service governance, while Integrity360 focuses on DevSecOps and cloud posture for software-as-a-service vendors. Strategic partnerships increasingly determine success. BT Security wraps Microsoft Sentinel analytics into its managed extended detection and response stack, giving clients unified insight across on-premises and multi-cloud assets. BAE Systems Digital Intelligence leverages sovereign data-handling assurances to secure defense contracts that require classified threat intelligence.
Innovation hotspots revolve around operational technology isolation, consumption-based licensing, and autonomous response. Darktrace’s 2026 product launch, which shields programmable logic controllers without halting production, exemplifies the trend toward harmonizing IT and OT security. Meanwhile, Immersive Labs trains cyber teams via gamified simulations, addressing talent shortages that otherwise impede technology rollouts. Certification schemes from the UK Cyber Security Council introduce standardized professional tiers, reducing vendor differentiation based solely on staffing credentials and pivoting competitive emphasis to the measurable efficacy of detection algorithms and integration breadth.
UK Cybersecurity Industry Leaders
Darktrace plc
Sophos Group plc
NCC Group plc
BAE Systems Digital Intelligence
BT Group plc (BT Security)
- *Disclaimer: Major Players sorted in no particular order

Market Opportunities and Future Outlook
Public-sector and regulated-industry programs are creating practical whitespace for vendors that can package measurable controls, continuous assurance, and supplier governance into deployable offerings. The Government Cyber Action Plan (January 2026) adds momentum to modernization across public services via funded uplift (GBP 210 million), supporting near-term demand for identity-first architectures, security monitoring, and tools that streamline evidence collection for audits and incident reporting. At the same time, the Cyber Security and Resilience (Network and Information Systems) Bill (2024-26) expands the compliance perimeter by bringing additional digital infrastructure such as data centres into scope, which increases requirements around vulnerability management, incident readiness, and third-party risk controls.
A second opportunity layer is building around government-industry coordination on resilience and AI-enabled defense. The Cyber Resilience Pledge encourages board-level oversight, participation in NCSC services such as Early Warning, and Cyber Essentials adoption across supply chains, supporting scalable managed services and simplified compliance bundles for large enterprises and their SME suppliers. At CYBERUK 2026, the government also highlighted new funding (GBP 90 million) and collaboration with frontier AI companies, alongside the NCSC National Cyber Defence Capability agenda. This broad focus creates room for UK-focused providers to productize AI-assisted detection, response automation, and secure-by-design integrations that address both IT and OT environments.
Recent Industry Developments
- July 2026: Sophos launched Sophos Fusion, positioned as an AI-native cybersecurity defense system, with general availability staged from August to October 2026. The release reinforces platform consolidation around AI-assisted detection and response workflows, supporting buyers who want fewer tools with unified policy and telemetry.
- June 2026: Sophos announced the general availability of Sophos Backup and Recovery, powered by Rubrik Cyber Resilience, for Microsoft 365 environments. The company linked protection and recovery into mainstream SaaS productivity stacks, aligning security spend with resilience outcomes as ransomware and business interruption risks rise.
- December 2025: Sophos completed the acquisition of Secureworks' managed detection and response business for USD 450 million. The deal expanded Sophos' MDR scale and delivery capacity, intensifying competition for multi-year managed security contracts among UK mid-market and regulated customers.


Research Methodology Framework and Report Scope
Market Definition and Coverage
This market covers spending in the United Kingdom on cybersecurity products and services that prevent, detect, and respond to digital threats across networks, endpoints, applications, cloud workloads, and data, as purchased by organizations and public bodies.
Scope exclusions: It excludes cyber insurance premiums and non-cyber IT spend that is not primarily meant for security outcomes.
Segmentation Overview
- By Offering
- Solutions
- Application Security
- Cloud Security
- Data Security
- Identity and Access Management
- Infrastructure Protection
- Integrated Risk Management
- Network Security
- End-point Security
- Services
- Professional Services
- Managed Services
- Solutions
- By Deployment Mode
- On-Premise
- Cloud
- By End-user Industry
- Banking, Financial Services, and Insurance (BFSI)
- Healthcare and Life Sciences
- IT and Telecommunication
- Government and Public Administration
- Industrial Manufacturing
- Retail and E-Commerce
- Energy and Utilities
- Transportation and Logistics
- Other End-User Industries
- By Organization Size
- Large Enterprises
- Small and Medium Enterprises (SMEs)
Data Sources, Market Sizing, and Validation
Desk Research
Desk work starts by grounding the UK demand environment and the policy context, because cybersecurity budgets are often tied to compliance pressure and incident trends. We refer to public sources such as the UK Government Cyber Security Breaches Survey, National Cyber Security Centre publications, Ofcom updates tied to telecom security, and Office for National Statistics business and digital economy indicators.
To keep the model connected to how money flows, we also review items like company annual reports, investor presentations, and reputable press coverage about large breach events and response programs. When needed, we use paid subscriptions for company financials and intelligence, news and financials, patent databases, and public contracts and tenders to spot deal patterns and timing. The sources noted above are illustrative rather than exhaustive, and other references are also used for data collection, cross-checks, and research clarification.
Primary Interviews and Surveys
Primary inputs are captured through expert interviews and structured surveys with buyers, channel participants, and subject matter specialists who track cybersecurity spending decisions in the UK. We cover a mix of regulated and non-regulated industries, and the discussions are used to confirm what is being budgeted, how cloud security adoption is changing, and where pricing is moving, before final assumptions are locked.
Distribution of primary research fieldwork respondents
| Company type | Respondent position | Region |
|---|---|---|
| Top tier: 35% | CXOs: 22% | |
| Mid tier: 43% | Functional/Unit leaders: 22% | |
| Smaller Players: 22% | Managers: 56% |
Market-Sizing & Forecasting
Sizing is built using a top-down and bottom-up mix, where UK cybersecurity demand is reconstructed from IT and digital spend indicators, followed by security allocation ratios that are adjusted by sector risk and compliance intensity. To keep the totals practical, we corroborate results with selective bottom-up checks, such as sampled supplier revenue splits tied to UK exposure, channel feedback on deal sizes, and simple volume times ASP tests for commonly procured security services.
Key inputs we use include the pace of cloud migration and hybrid architecture adoption, managed security service take-up, incident frequency signals and response intensity, regulatory milestones that influence spend timing, and enterprise mix by size (because spending per organization differs a lot). Where UK-only revenue is not cleanly disclosed, gaps are handled through geography allocation using employee and customer footprint indicators, which are then sanity checked during expert calls.
For forecasting, scenario analysis is used, since security budgets can step up after major incidents and also get delayed in weak macro periods. Assumptions are reviewed with practitioners so the forward path reflects expected project pipelines, contract renewals, and realistic price progression rather than a straight-line trend.
Data Validation & Update Cycle
Validation is done through triangulation across independent signals, and then through variance checks so unusually high or low growth points are explained before sign-off. We compare model outputs against proxies like public sector security programs, breach trend signals, and disclosed security spend commentary in filings, which helps flag mismatches early.
Before publishing, a multi-step analyst review is run, and follow-up outreach is triggered when an assumption materially changes or when a large deal or policy change is noticed. Reports are refreshed annually, with interim updates for material events, and a final pre-delivery pass is done so clients receive the latest updated view.
黑料不打烊's UK Cybersecurity Market Estimate Compared With Other Published Estimates
Published UK cybersecurity market values can differ even when the topic label looks the same, because each publisher may count a different mix of solutions versus services, apply different currency timing, and choose different base years for what they call the current market.
The biggest gaps usually come from scope coverage around what gets counted as cybersecurity, how managed services are treated versus in-house security labor, and whether adjacent IT items are bundled in. Differences also show up when one model assumes faster cloud security ramp-up, or when exchange-rate conversion is taken at a single point rather than averaged over the year, which changes USD totals for the UK.
Benchmark comparison
| Source | Market Size | Gaps in Research Methodology |
|---|---|---|
| 黑料不打烊 | USD 18.36 B (2026) | |
| Industry Association A | USD 16.90 B (2026) | Often uses narrower accounting that emphasizes buyer-side security software and excludes part of managed security and incident response retainers, which can understate services-heavy UK demand. |
| Global Consultancy B | USD 21.40 B (2026) | Typically folds in adjacent IT risk and resilience items and may apply a more aggressive cloud security uplift, which can push totals higher when bundled spend is treated as cybersecurity. |
The table shows a clear spread around the same year, and under 黑料不打烊's scope the total counts only cybersecurity solutions and services sold into the UK, while excluding cyber insurance and non-security IT operations spend. By anchoring the math to practical demand signals and then rechecking assumptions through interviews, we end up with a value that can be traced back to repeatable steps.


Key Questions Answered in the Report
What is the forecast value of the UK cybersecurity market in 2031?
The UK cybersecurity market size was valued at USD 14.77 billion in 2025 and estimated to grow from USD 16.27 billion in 2026 to USD 25.13 billion by 2031, reflecting a 9.09% CAGR during the forecast period (2026-2031).
Which deployment mode is growing fastest across UK organizations?
Cloud-delivered security solutions are expanding at a 12.32% CAGR as hybrid work cements perimeter dissolution.
Why are SMEs increasing cybersecurity budgets?
Insurers now demand multi-factor authentication, patch management, and offline backups before issuing cyber policies, pushing SMEs toward managed service bundles.
Which industry segment shows the highest growth through 2031?
Healthcare and life sciences industry spending is set to climb at a 13.67% CAGR due to government-funded modernization and ransomware risk.
How severe is the UK cyber-skills shortage?
A significant number of roles remained unfilled in 2025, causing salary inflation and extending project timelines.
What role does artificial intelligence play in modern UK defenses?
Enterprises deploy AI analytics to baseline normal behavior and isolate anomalies within minutes, shrinking adversary dwell time.
Page last updated on:


