
Middle East Cybersecurity Market Size and Share
Market Overview
| Study Period | 2021 - 2031 |
|---|---|
| Forecast Data Period | 2026 - 2031 |
| Base Year Market Size (2025) | USD 20.55 Billion |
| Market Size (2026) | USD 23.54 Billion |
| Market Size (2031) | USD 46.39 Billion |
| Growth Rate (2026 - 2031) | 14.55 % |
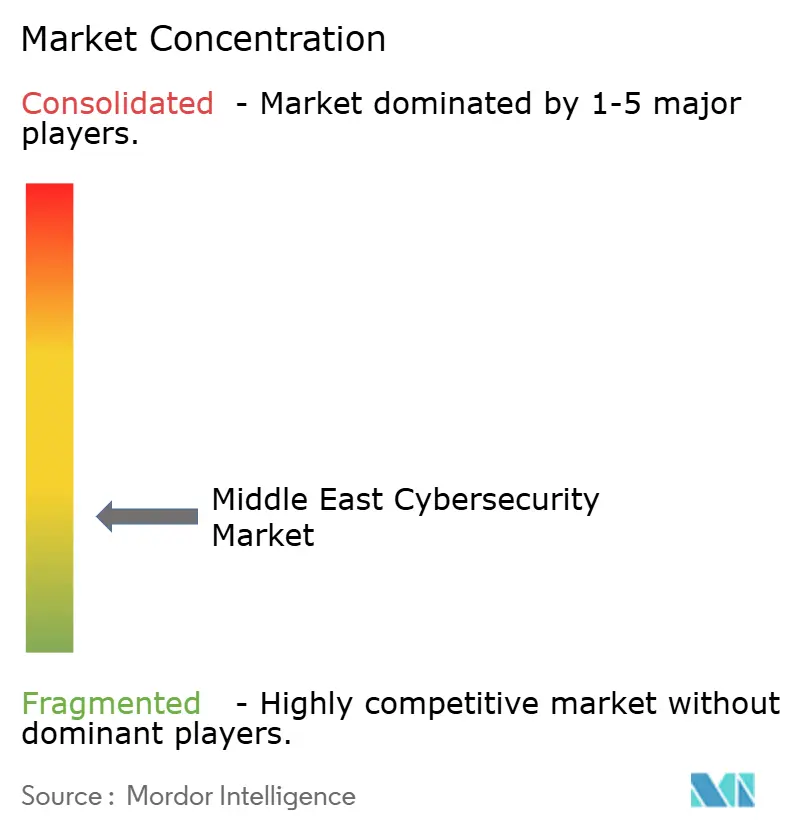
| Market Concentration | Medium |
Major Players *Disclaimer: Major Players sorted in no particular order Image ? 黑料不打烊. Reuse requires attribution under CC BY 4.0. | |
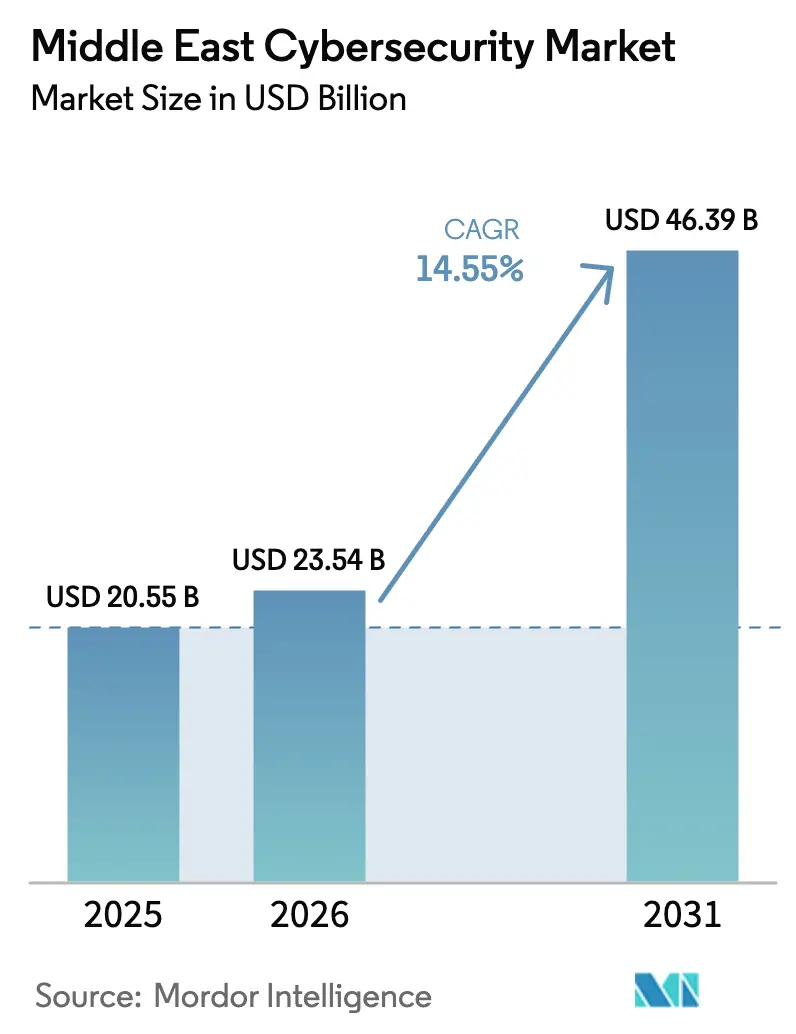
Middle East Cybersecurity Market Analysis by 黑料不打烊
The Middle East cybersecurity market size was valued at USD 20.55 billion in 2025 and estimated to grow from USD 23.54 billion in 2026 to reach USD 46.39 billion by 2031, at a CAGR of 14.55% during the forecast period (2026-2031). Accelerated digitalization, persistent nation-state attacks, and mandatory compliance spending under national transformation programs are fueling demand. Critical-infrastructure breaches such as the two-year Iranian infiltration of regional operational networks have shifted budgets from discretionary tools to zero-trust platforms. Government “Vision” agendas in the GCC are transforming cybersecurity into a baseline cost of doing business, while cloud migration and AI adoption across public agencies create new attack surfaces that require specialized defenses. Talent shortages and fragmented data-sovereignty rules temper progress, but a growing pool of local managed-security providers and international partnerships is beginning to ease implementation frictions.
Key Report Takeaways
- By offering, solutions commanded a 52.12% share of the Middle East cybersecurity market size in 2025, while services are forecast to grow at a 18.45% CAGR between 2026 and 2031.
- By deployment mode, cloud installations accounted for 73.06% of the Middle East cybersecurity market in 2025. Cloud-based deployments are projected to grow at an 18.32% CAGR through 2031.
- By organization size, large enterprises captured 51.96% of the Middle East cybersecurity market share in 2025, and SMEs are advancing at a 17.21% CAGR through 2031.
- By end user, the BFSI sector accounted for 21.02% of revenue in 2025; healthcare is projected to compound at a 20.12% CAGR through 2031.
- By country, Saudi Arabia in the Middle East has a 29.62% market share in cybersecurity in 2025, whereas the United Arab Emirates (UAE) is expected to expand at a 17.46% CAGR through 2031.
Note: Market size and forecast figures in this report are generated using 黑料不打烊’s proprietary estimation framework, updated with the latest available data and insights as of 2026.
Market Trends and Insights
Drivers Impact Analysis of Middle East Cybersecurity Market*
| Driver | (~) % Impact on CAGR Forecast | Geographic Relevance | Impact Timeline |
|---|---|---|---|
| Surge in Nation-State and Critical-Infrastructure Attacks | +3.2% | UAE, Saudi Arabia | Medium term (2-4 years) |
| Government "Vision" Programmes Mandating Cyber Budgets | +2.8% | GCC core | Long term (≥4 years) |
| Cloud-First and SaaS Adoption Across GCC Public Sector | +2.1% | UAE, Saudi Arabia, Qatar | Short term (≤2 years) |
| AI-Driven Security Analytics Lowering MTTR | +1.9% | UAE, Saudi Arabia | Medium term (2-4 years) |
| M&A Wave Among Local MSSPs Creating Bundled Offerings | +1.4% | UAE, Saudi Arabia | Short term (≤2 years) |
| Oil-and-Gas OT Retrofit to Zero-Trust Architectures | +1.6% | Saudi Arabia, UAE, Kuwait, Oman | Long term (≥4 years) |
| Source: 黑料不打烊 | |||
Surge in Nation-State and Critical-Infrastructure Attacks
State-sponsored groups have shifted from smash-and-grab intrusions to patient, multi-year footholds in operational networks, as illustrated by the Lemon Sandstorm campaign that exploited VPN flaws across regional utilities.[1]Lemos, Robert, “Lemon Sandstorm Reveals Risks to Middle East Infrastructure,” Dark Reading, darkreading.com Iranian-linked actors maintained covert access for up to 24 months, highlighting the strategic value that adversaries placed on disruption capabilities and long-term network surveillance. In response, governments strengthened real-time threat intelligence exchanges and improved cross-border coordination. For instance, the UAE Cyber Security Council’s pact with Group-IB coordinated incident response playbooks across 15 jurisdictions, supporting faster detection, containment, and remediation of cyber threats. As a result, heightened geopolitical tensions continued to drive premium spending on endpoint hardening, OT visibility tools, and forensics services across the Middle East cybersecurity market.
Government “Vision” Programmes Mandating Cyber Budgets
Legally binding national transformation roadmaps in Saudi Arabia, the UAE, and Qatar have positioned cybersecurity as a core national security priority. These programs are moving cybersecurity investments from discretionary technology spending to mandated budget allocations across public and private entities. As a result, organizations are converting previously optional licenses, compliance tools, and security services into enforceable budget line items to meet regulatory and operational requirements. Saudi regulations introduced in December 2024 stipulated penalties of up to SAR 25 million (USD 6.60 million) for non-compliance, effectively strengthening enterprise accountability and supporting multi-year cybersecurity procurement pipelines.[2]Two Birds, “Saudi Arabia: National Cybersecurity Authority Regulations 2024,” twobirds.com The UAE targeted AI to contribute 20% to non-oil GDP, which increased the need for secure digital infrastructure across government services, enterprises, and critical industries. Consequently, every digital service rollout must undergo security accreditation before launch. These mandatory cybersecurity baselines are shifting the Middle East cybersecurity market from project-based spending to a recurring budget model, as organizations must continuously invest in compliance, monitoring, risk management, and cyber resilience.
Cloud-First and SaaS Adoption Across GCC Public Sector
Chief AI officers in UAE ministries and blockchain pilots in Saudi banks are accelerating the migration of sensitive data to shared cloud infrastructures. This shift is increasing the need for advanced cloud security controls, identity-based access management, and secure access service edge (SASE) platforms to protect distributed workloads and users. As public sector entities across the GCC expand their use of cloud-first strategies and software-as-a-service (SaaS) applications, cybersecurity investments are becoming essential to support secure digital transformation, regulatory compliance, and operational resilience. Google Cloud’s center of excellence in Abu Dhabi is projected to help avert USD 6.8 billion in cybercrime losses by 2030, underscoring the economic value of proactive cybersecurity investment.[3]UAE Cyber Security Council, “Empowering Cyber Defense: UAE and Google Cloud to Collaborate on Cybersecurity,” googlecloudpresscorner.com Data sovereignty requirements continue to influence cloud adoption decisions, but confidential computing deployments are helping agencies encrypt data while in use, reducing migration risks and supporting the secure adoption of shared infrastructure.
AI-Driven Security Analytics Lowering MTTR
Regional enterprises are increasingly adopting machine-learning-based telemetry to close detection gaps without significantly expanding cybersecurity teams. This approach helps organizations improve threat visibility, automate alert triage, and reduce mean time to respond (MTTR) across complex IT and operational environments. Surveys show that 99% of UAE organizations recognized AI’s benefits in strengthening cyber resilience, while 49% planned to allocate additional budgets specifically for analytics use-cases.[4]Zawya, “UAE organisations ramp up AI investments, boosting data compliance and cyber resilience,” zawya.com Banks are deploying behavioral analytics models to enhance fraud prevention and support compliance with SAMA’s supervisory guidance. Vendors that provide model-agnostic data pipelines, scalable analytics capabilities, and local-language threat intelligence libraries are gaining traction as enterprises prioritize faster detection, contextual response, and operational efficiency.
Restraints Impact Analysis of Middle East Cybersecurity Market*
| Restraint | (~) % Impact on CAGR Forecast | Geographic Relevance | Impact Timeline |
|---|---|---|---|
| Persistent Talent Gap and Double-Digit Wage Inflation | -2.4% | GCC core, especially Saudi Arabia and UAE | Medium term (2-4 years) |
| Fragmented Data-Sovereignty Laws Across GCC and Levant | -1.8% | Region-wide, varies by country | Long term (≥4 years) |
| Air-Gapped Legacy SCADA Delaying Operational-Technology Upgrades | -1.2% | Saudi Arabia, UAE, Kuwait, Oman | Long term (≥4 years) |
| Unmanaged Shadow IT Across SME Supply Chains | -0.8% | GCC core | Medium term (2-4 years) |
| Source: 黑料不打烊 | |||
Persistent Talent Gap and Double-Digit Wage Inflation
Rapid digitalization outpaced the supply of skilled cybersecurity professionals, creating a persistent talent gap that challenged the growth of the Middle East cybersecurity market. Power utilities in Saudi Arabia struggled to fill key roles, even as they raised salaries at double-digit rates. This wage inflation increased operating costs, compressed margins, and delayed cybersecurity project timelines, limiting utilities' ability to scale security programs efficiently. The shortage also affected the timely deployment of advanced solutions across critical infrastructure, particularly in areas requiring specialized expertise. Although universities expanded their course offerings, expertise in AI, cloud security, and incident response remained scarce, making it difficult for organizations to build resilient cybersecurity capabilities and sustain market growth.
Fragmented Data-Sovereignty Laws Across GCC and Levant
Fragmented data sovereignty and localization statutes across the GCC and Levant require multinational enterprises and cybersecurity service providers to operate parallel data environments, increasing architectural complexity, compliance costs, and implementation timelines. The UAE’s data protection law includes multiple sectoral exemptions, while Saudi regulations continue to require specific data classes to remain onshore. This regulatory divergence limits economies of scale for regional service rollouts and makes it more difficult for vendors to deploy standardized cybersecurity platforms across multiple jurisdictions. As a result, organizations often need customized security architectures, localized data storage, and country-specific compliance controls, which can delay procurement decisions and increase total cost of ownership. These factors have constrained the growth of the Middle East cybersecurity market by slowing cloud-based security adoption, complicating managed security service delivery, and reducing operational efficiency for both buyers and providers.
*Our forecasts treat driver/restraint impacts as directional, not additive. The impact forecasts reflect baseline growth, mix effects, and variable interactions.
Middle East Cybersecurity Market Segment Analysis
By Offering:
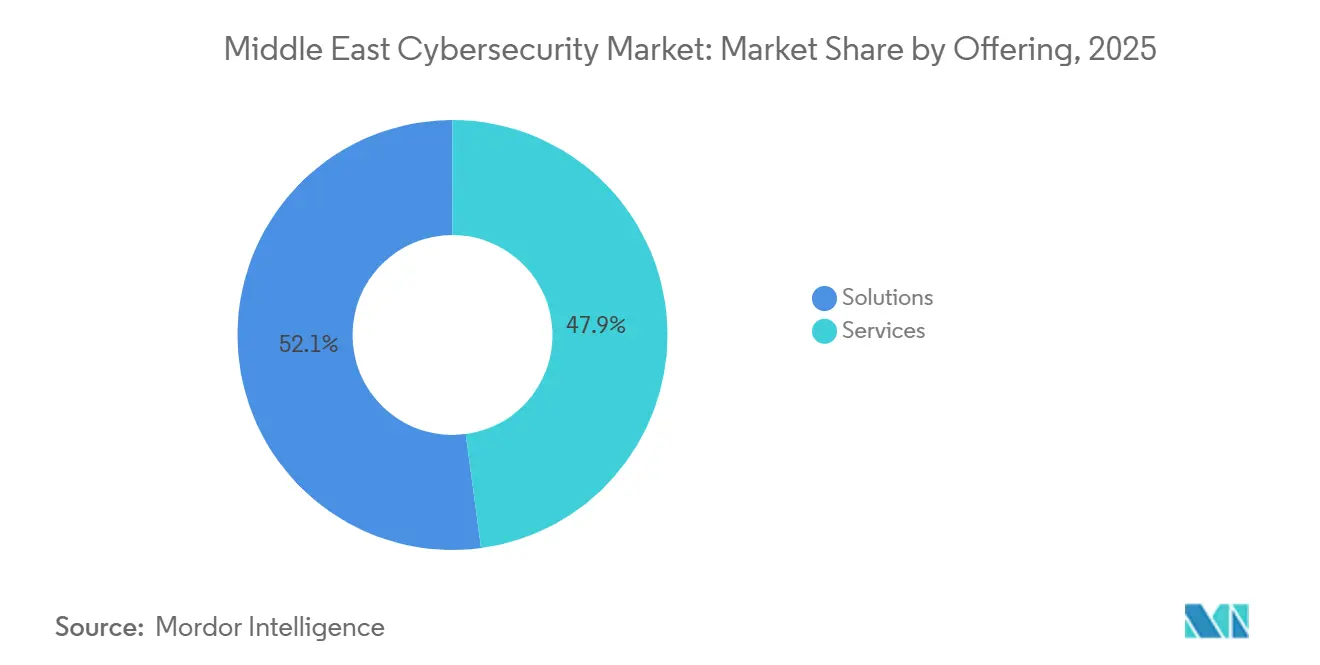
Solutions Accelerate Past ServicesSolutions accounted for 52.12% of the Middle East cybersecurity market size in 2025, while services are forecast to register a CAGR of 18.45% during 2026-2031. Services revenue is expanding at a faster pace than solutions revenue as enterprises move away from incident-driven outsourcing and increasingly adopt platform-centric prevention models. This shift reflects a broader focus on proactive cybersecurity management, continuous monitoring, and integrated defense capabilities. Demand remains concentrated in cloud security posture management, application shielding, and identity orchestration, as these capabilities support the implementation of zero-trust policies across enterprise environments. High-profile infrastructure breaches have also accelerated the inclusion of real-time visibility tools and anomaly-detection engines in procurement plans, as organizations prioritize faster threat identification and response.
At the same time, professional services teams continue to address a specialized niche in compliance audits and red-teaming, particularly among organizations that require external validation of security controls and regulatory readiness. However, managed security contracts face pricing pressure as larger customers increasingly insource security operations centers to gain greater control over security processes, data visibility, and incident response. AI-native vendors, such as Corgea, secured USD 2.6 million to develop automated vulnerability-triage engines adapted to Arabic-language code bases, underscoring the innovation now strengthening the solutions pipeline and supporting the market’s shift toward more automated and context-aware cybersecurity capabilities.


By Deployment Mode:
Cloud Gains Despite Sovereignty ConcernsCloud workloads accounted for 73.06% of the Middle East cybersecurity market in 2025 and are projected to grow at a 18.32% CAGR through 2031. GCC ministries have adopted “cloud-first” charters to modernize citizen services, improve operational efficiency, and strengthen digital service delivery. This shift has increased the adoption of SASE and workload-encryption gateways, as public-sector entities and enterprises prioritize secure access, data protection, and scalable cloud operations. Confidential computing options now offer hardware-based controls that help organizations meet regulatory requirements while retaining the cost and scalability benefits of cloud infrastructure.
On-premises deployments remain the preferred model for core banking and defense networks, where organizations must comply with stringent data classification, sovereignty, and security requirements. Hybrid models are also gaining traction as institutions balance regulatory compliance with the need for advanced digital capabilities. Saudi banks now route interbank blockchain transfers through local nodes while storing analytics workloads in sovereign clouds. This dual-stack approach protects critical data residency requirements while enabling AI-driven fraud monitoring, faster analytics, and more flexible operations in elastic cloud environments.
By Organization Size:
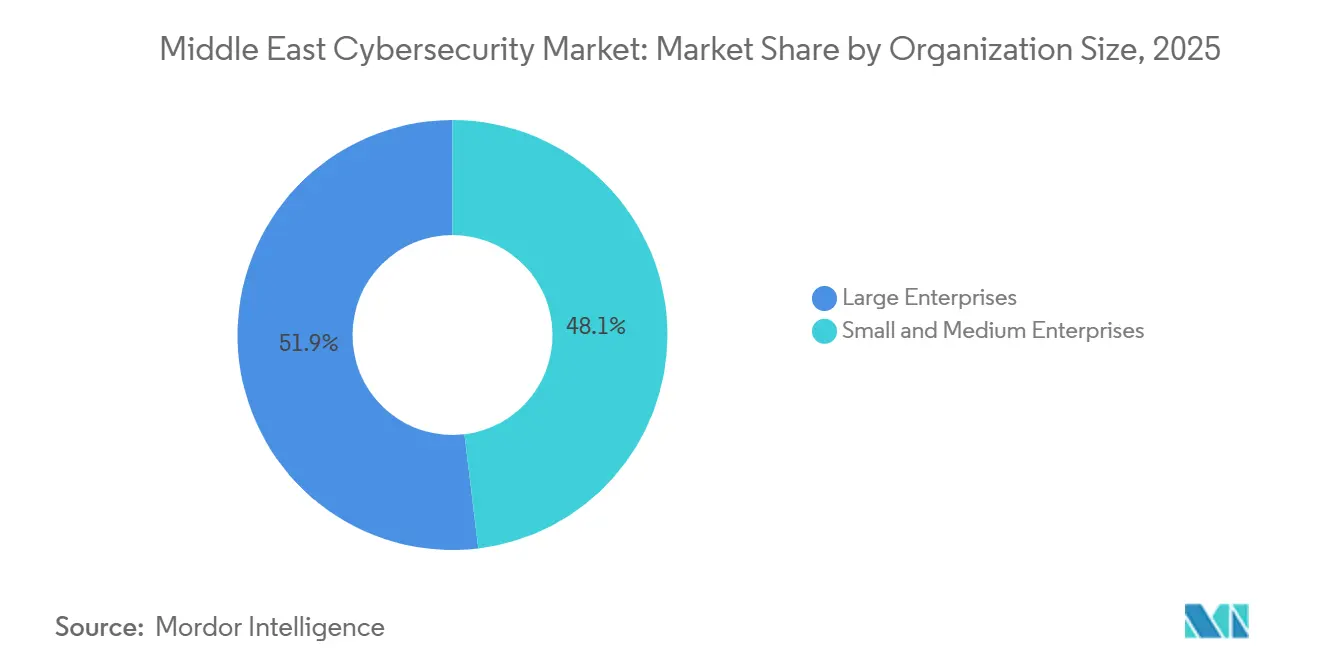
SMEs Drive Unexpected GrowthLarge enterprises accounted for 51.96% of revenue in 2025, while SMEs are projected to expand at a CAGR of 17.21% as cybersecurity awareness increases and turnkey solution bundles reduce entry barriers. Regional entrepreneurship agendas, including Monsha’at’s financing schemes, continue to support the creation of digital-first firms that consider cybersecurity a prerequisite for licensing and business operations. In response to this demand, vendors are packaging endpoint, email, and cloud-access security into multi-tenant consoles with consumption-based pricing, enabling organizations to adopt integrated protection with greater flexibility and lower upfront investment.
Although large enterprises already operate relatively mature cybersecurity frameworks, they are facing new OT challenges across oil, gas, and petrochemicals, where 60% of operators consider operational threats more severe than IT threats. As a result, their cybersecurity spending is shifting from traditional perimeter equipment toward segmentation gateways and identity governance solutions that extend across refinery control networks. This transition reflects a stronger focus on protecting critical operational environments, improving access control, and reducing risks across interconnected industrial systems.
By End User:
Healthcare Emerges as Growth LeaderHealthcare spending is projected to increase at a CAGR of 20.12% through 2031, supported by the continued adoption of digitized patient workflows, telemedicine platforms, and IoT-enabled diagnostics. These technologies improve clinical efficiency and patient access but also expand the cyberattack surface across healthcare networks. Ransomware incidents targeting hospital chains have led regulators to strengthen requirements for continuous monitoring and encrypted transfer of patient records. As a result, healthcare organizations are increasing their focus on network isolation, anomaly detection, and stronger cybersecurity controls. The implementation of Industry 4.0 principles in smart clinics is also driving higher demand for identity management and micro-segmentation solutions to secure connected medical environments.
Conversely, the Banking, Financial Services, and Insurance (BFSI) sector accounted for 21.02% of revenue in 2025, supported by capital adequacy rules that required institutions to continuously enhance their cyber controls. Regional banks integrated behavioral AI solutions to detect fraud in real time and strengthen compliance with SAMA’s supervisory mandates. Energy and Utilities companies directed budgets toward zero-trust retrofits to improve the resilience of critical infrastructure, while Manufacturing companies deployed supply-chain security solutions to protect connected production lines and reduce risks across industrial networks.
Geography Analysis
Saudi Arabia Cybersecurity Market
Saudi Arabia was the largest market in the region, accounting for 29.62% of the market share in 2025. Large-scale investments in securing oil and gas infrastructure, financial services, and government systems under Vision 2030 drove its leading position. The country also advanced sovereign cloud adoption and strengthened national cybersecurity frameworks, which reinforced its role as the anchor market for vendors and service providers. These initiatives supported strong demand for cybersecurity solutions across critical infrastructure, public sector, and enterprise environments.
United Arab Emirates Cybersecurity Market
The United Arab Emirates (UAE) is the fastest-growing market, projected to register a CAGR of 17.46% between 2026 and 2031. Smart city initiatives in Dubai and Abu Dhabi, strong regulatory enforcement, and the rapid adoption of AI-enabled cybersecurity solutions are expected to drive this growth. The UAE’s position as a regional technology hub continues to support innovation, digital transformation, and advanced security deployments across the Middle East. Rising investments in cloud security, threat intelligence, and managed security services are also expected to strengthen the country’s cybersecurity market during the forecast period.
GCC Cybersecurity Market
Other countries, including Qatar, Kuwait, and Bahrain, also contribute to regional growth. National cybersecurity strategies, compliance mandates, and increasing reliance on managed security services support their markets. Although these countries are smaller in scale than Saudi Arabia and the UAE, they are steadily improving their cybersecurity posture through investments in digital infrastructure, regulatory modernization, and critical asset protection. These efforts continue to expand opportunities for vendors and service providers across the region.
Regulatory Landscape
Cybersecurity regulation across the Middle East is tightening around provider licensing, critical-infrastructure assurance, and faster incident reporting. In Saudi Arabia, the National Cybersecurity Authority (NCA) advanced RFCS-1: 2026 (Regulatory Framework for Licensing Cybersecurity Services, Products and Solutions), moving the market toward formal oversight of cybersecurity vendors and service providers. This adds compliance expectations for both local MSSPs and multinationals serving government and other regulated sectors.
The UAE is also formalizing cyber governance under national strategy programs, including government-procurement oriented controls such as SBOM-style transparency and accreditation-led access for suppliers serving critical information infrastructure. Outside the GCC core, Oman enacted a Cybercrime Law through Royal Decree 61/2026, effective June 2026, reinforcing legal consequences for cyber offenses and strengthening the enforcement backdrop behind enterprise investment in monitoring, incident response, and forensics. Across countries, data-sovereignty requirements and national accreditation approaches are increasingly shaping go-to-market models, with vendors pushed toward in-country delivery, local partnerships, and auditable control mappings for public sector, BFSI, and critical-infrastructure buyers.
Value Chain Analysis
The Middle East cybersecurity value chain starts with global and regional technology suppliers (network security, endpoint, IAM, cloud security, OT security, and threat intelligence), followed by distributors and systems integrators that localize deployments for regulated environments, and then MSSPs that run SOC operations, MDR, and incident response on behalf of enterprises and public agencies. Government and critical-infrastructure buyers heavily influence demand, where procurement often routes through accredited partners and requires data residency, local support, and compliance documentation. This structure supports a higher share of services around architecture design, control validation, and continuous monitoring.
Public-private collaboration is a defining midstream layer in the region, with the UAE Cyber Security Council working with multinational vendors to stand up local capability hubs, including innovation centers and OT-focused centers of excellence. This tightens feedback loops between policy requirements, product configuration, and skills development. Localization of delivery, including sovereign cloud operating models and local data-center footprints, and assurance frameworks governing high-stakes technology transfer, such as the Intergovernmental Assurance Agreement (IGAA) referenced around Microsoft and G42, are increasingly embedded in how solutions are packaged, operated, and supported across the region.
Competitive Landscape
Global suppliers such as Cisco, Palo Alto Networks, and Fortinet compete with local champions, including DarkMatter, Help AG, and CPX, in the Middle East cybersecurity market, which remains moderately fragmented. G42 acquired CPX in February 2025, integrating AI infrastructure with defensive tooling and highlighting how cross-domain capabilities have become an important differentiator for market leaders. The transaction strengthened the link between advanced computing capabilities and cybersecurity operations, reinforcing the market shift toward integrated platforms that can support threat detection, response, and resilience. DarkMatter’s government-heavy order book, estimated to account for 80% of its revenue, demonstrates the continued importance of sovereign trust, particularly among public-sector and critical-infrastructure customers.
Saudi firm Cipher secured USD 13.3 million in funding to expand its penetration testing and incident response teams, reflecting growing demand for specialized cybersecurity services across the region. VC funding is increasingly shifting toward AI-driven platforms that can address Arabic-language datasets, regional threat patterns, and local compliance requirements. Strategic alliances between energy OEMs and cyber vendors are also gaining traction, with companies such as Palo Alto Networks partnering with SLB to embed security into industrial-control upgrades. These partnerships indicate that cybersecurity is becoming a core component of industrial modernization, particularly in sectors where operational continuity, safety, and regulatory compliance are critical.
Price competition is intensifying in commoditized endpoint niches as vendors compete on scale, bundled features, and managed service capabilities. However, premium margins persist in specialized areas such as OT segmentation gateways, confidential computing chips, and AI threat-hunting modules, where buyers prioritize performance, resilience, and compliance assurance over price. The rise of bundled MSSP offerings and sovereign-cloud SOCs is likely to reduce the share of pure-play consulting firms, especially as customers seek integrated security operations, localized data handling, and continuous monitoring. Consequently, success will depend on hybrid delivery models, locally skilled staffing, and demonstrable compliance mappings that align cybersecurity solutions with regional regulatory and operational requirements.
Middle East Cybersecurity Industry Leaders
IBM Corporation
Fortinet Inc.
Cisco Systems Inc.
Trend Micro Inc.
Microsoft Corporation
- *Disclaimer: Major Players sorted in no particular order
Middle East Cybersecurity Market Companies Covered in this Report
- IBM Corporation
- Cisco Systems Inc.
- Fortinet Inc.
- Microsoft Corporation
- Trend Micro Incorporated
- Palo Alto Networks Inc.
- Check Point Software Technologies Ltd.
- Broadcom Ltd. (Symantec)
- Dell Technologies Inc.
- Intel Corporation
- McAfee LLC
- Huawei Technologies Co. Ltd.
- Zscaler Inc.
- DarkMatter Group
- Help AG (e&)
- CPX Holding (UAE)
- StarLink ME
- Cyway LLC
- BAE Systems AI
- Kaspersky Lab

Market Opportunities and Future Outlook
A near-term whitespace area is compliance-aligned supplier enablement, as regulators and critical-infrastructure owners raise expectations for accredited delivery, breach reporting discipline, and supply-chain transparency. Saudi Arabia's NCA RFCS-1: 2026 increases the importance of licensed and monitored cybersecurity offerings, creating room for vendors and partners that can operationalize controls through auditable managed services, readiness assessments, and localization-friendly architectures. In the UAE, national programs and procurement-driven requirements continue to reinforce demand for security capabilities that attach directly to digital government rollout cycles, including secure cloud adoption and AI governance controls.
AI security, OT/ICS protection, and local workforce development also represent active opportunity lanes with visible market actions. In 2026, IBM announced plans for a joint Innovation Center with the UAE Cyber Security Council, and Fortinet formalized an MoU with the same body, including local capability building such as a local data center and a FortiGuard Center of Excellence. These moves reflect customer preference for in-country expertise, threat intelligence, and sovereign-aligned operating models. Investments in regional AI infrastructure, including Microsoft and G42 under an assurance framework (IGAA), further increase demand for cloud security posture management, identity-centric zero trust, and model and data protection controls that can be delivered within local regulatory constraints.
Recent Industry Developments in Middle East Cybersecurity Market
- June 2026: Trend Micro (TrendAI) launched TrendAI enterprise AI security business in the United Arab Emirates. The launch expands AI security offerings in UAE market and strengthens local AI governance and security capabilities in UAE.
- May 2026: IBM announced a joint Innovation Center in Abu Dhabi with the UAE Cybersecurity Council. The collaboration signals trusted AI and cybersecurity innovation in the region and anchors sovereign AI security initiatives and regional R&D in UAE.
- May 2026: Fortinet formalized an MoU with the UAE Cyber Security Council to advance national cybersecurity capabilities. The agreement supports data sovereignty and local cybersecurity capacity and establishes local data center and security collaboration to boost regional resilience.


Middle East Cybersecurity Market Report Scope and Research Methodology
Market Definition and Coverage
For this methodology, the market covers spending on cybersecurity solutions and services used to prevent, detect, and respond to digital threats across Middle East organizations in both public and private sectors.
Scope exclusions: Pure physical security, non-cyber safety systems, and general IT hardware that is not bought mainly for security outcomes are not counted.
Segments Covered in This Report
- By Offering
- Solutions
- Application Security
- Cloud Security
- Data Security
- Identity and Access Management
- Infrastructure Protection
- Integrated Risk Management
- Network Security Equipment
- Endpoint Security
- Services
- Professional Services
- Managed Services
- Solutions
- By Deployment Mode
- Cloud
- On-premise
- By Organization Size
- Small and Medium Enterprises (SMEs)
- Large Enterprises
- By End-User Industry
- Banking, Financial Services, and Insurance (BFSI)
- Healthcare and Life Sciences
- IT and Telecommunication
- Government and Public Administration
- Retail and E-Commerce
- Energy and Utilities
- Industrial Manufacturing
- Other End-User Industries
- By Country
- Saudi Arabia
- United Arab Emirates
- Qatar
- Kuwait
- Bahrain
- Rest of Middle East
Data Sources, Market Sizing, and Validation
Desk Research
Desk research started with mapping the cyber risk surface and how regulations push budgets into security lines. We referenced public sources such as national cybersecurity agencies and regulators, telecom authorities, central bank circulars, and statistics bodies that report ICT and digital adoption indicators.
We also used disclosure-led sources such as annual reports, investor presentations, and press releases to map security priorities by sector, plus reputable media reporting on incidents and policy changes. For fill-in checks, we leaned on paid subscriptions for company financials and intelligence, news and financials, an import and export shipment-level database (for selected hardware-linked security categories), and patent databases to gauge product activity. The sources listed here are not exhaustive, and many other public documents and datasets were also used for collection, validation, and clarification.
Primary Interviews and Surveys
Primary work was used to test what desk sources could not show clearly, mainly how budgets split across tools, services, and deployment choices across different countries. We spoke with buyers, security leaders, service providers, and channel participants across the Gulf and other key Middle East markets so assumptions on adoption timing and pricing stayed realistic.
Distribution of primary research fieldwork respondents
| Company type | Respondent position |
|---|---|
| Top tier: 30% | CXOs: 13% |
| Mid tier: 54% | Functional/Unit leaders: 35% |
| Smaller Players: 16% | Managers: 52% |
Market-Sizing & Forecasting
Sizing began with a top-down build where regional IT and digitalization spend signals were converted into a cybersecurity demand pool using penetration and budget-share assumptions that were checked country by country. After forming the first total, we corroborated it with selective bottom-up approximations, including sampled price per user for endpoint and identity controls, cloud workload growth mapped to cloud security attach rates, and channel checks on managed service bundles. Where mismatches appeared, we adjusted the totals.
Inputs were kept practical and repeatable, including public cloud adoption pace, the number of regulated entities in banking and critical infrastructure, large program rollouts tied to national digital initiatives, reported breach intensity and response requirements, and the local mix of in-house teams versus outsourced SOC and managed services. Forecasts were produced using scenario analysis, where drivers such as regulation enforcement timing, cloud migration speed, and skills availability were varied, then aligned to the most common outlook shared during interviews.
Data Validation & Update Cycle
Validation was done by triangulating the model against independent signals such as ICT spend direction, cloud service expansion, public sector procurement patterns, and the observed pace of compliance-driven rollouts. Outliers were reviewed through variance checks across countries and end users, and follow-up calls were triggered when a key assumption shifted or when a new policy announcement changed timing.
Before sign-off, the work is reviewed in steps so the market totals, growth rates, and key assumptions remain consistent across sections. Reports are refreshed annually, and interim updates are made when material events occur, followed by a final pre-delivery pass to keep the numbers current.
黑料不打烊's Middle East Cybersecurity Market Size Measured Against Other Published Estimates
Published market sizes for Middle East cybersecurity can look far apart because the underlying definitions often differ, even when the topic label sounds similar. Differences typically come from whether a source tracks end-user spending versus vendor revenues, which countries are included, and whether IT risk management items beyond security are folded in.
Some published figures cover a wider geography like MENA or MEA and may also describe security and risk management spend that includes adjacent categories. In 黑料不打烊, the market total is counted as cybersecurity solutions and services within the Middle East report scope, and totals are refreshed around the stated base year so currency timing and price progression do not drift.
Benchmark comparison
| Source | Market Size | Gaps in Research Methodology |
|---|---|---|
| 黑料不打烊 | USD 20.55 B (2025) | |
| Global Advisory A | USD 3.30 B (2024) | Uses MENA end-user security and risk management spending, which can exclude Middle East countries outside its definition and can group in adjacent risk categories that are not treated as cybersecurity revenue. |
| Trade Journal B | USD 6.20 B (2024) | Represents MEA security products and services spending and explicitly excludes Israel, which changes the geography, and the year and spend-based lens makes it smaller than a Middle East market value model. |
The table shows that the spread is mainly driven by geography labels and what is being measured, which is spending versus a broader market value view. By keeping scope and year alignment explicit and then checking results against adoption and pricing signals, the final number stays traceable to clear steps that can be repeated.


Key Questions Answered in the Report
What is the current value of the Middle East cybersecurity market?
The market is valued at USD 20.55 billion in 2025, and USD 23.54 billion in 2026 and is on track to reach USD 46.39 billion by 2031 with a CAGR of 14.55%.
Which country leads regional spending on cybersecurity?
The United Arab Emirates holds the largest country share at 29.62% of 2025 revenue.
Which sector is growing fastest in cybersecurity demand?
Healthcare is expanding at a 20.12% CAGR through 2031 as hospitals digitalise and protect patient data.
How are national “Vision” programmes influencing budgets?
Regulations under initiatives such as Saudi Vision 2030 mandate minimum security controls, converting cybersecurity into a non-discretionary operating cost.
Why is cloud security becoming a priority despite data-residency rules?
Confidential-computing and sovereign-cloud models let agencies leverage elastic resources while keeping sensitive data under national jurisdiction.
What is the main barrier to faster market growth?
A persistent shortage of skilled cybersecurity professionals drives wage inflation and slows project rollouts, especially in Saudi Arabia and the UAE.
Page last updated on:


