
Market Overview
| Study Period | 2020 - 2031 |
|---|---|
| Forecast Data Period | 2026 - 2031 |
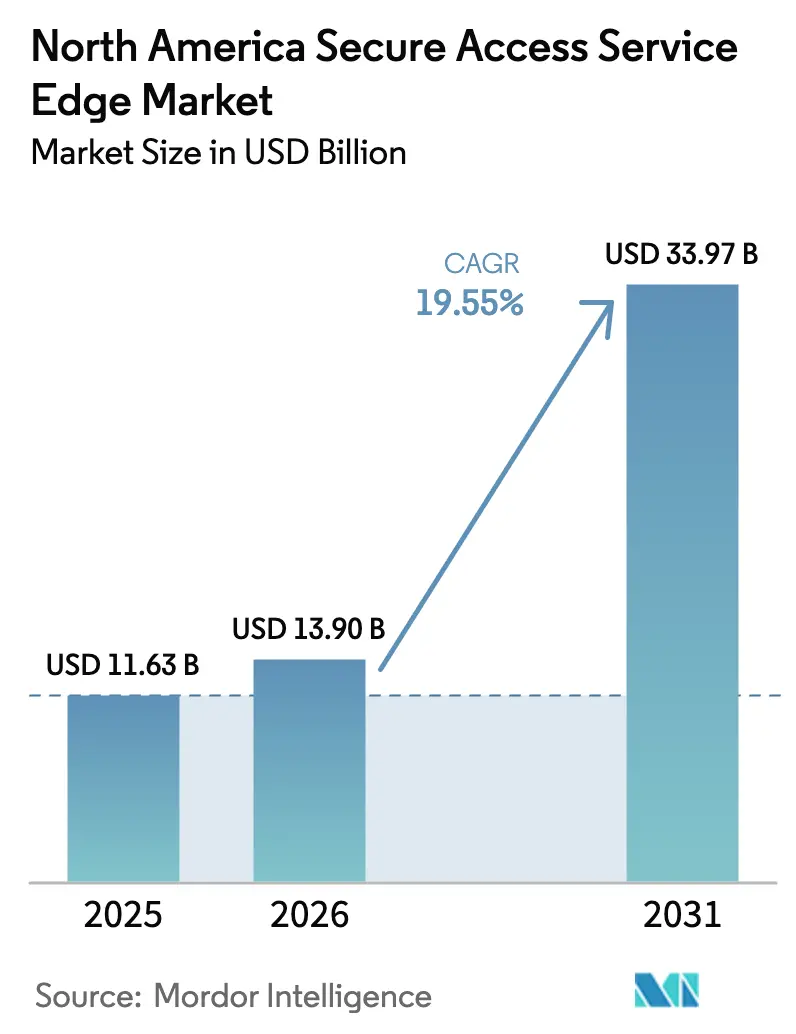
| Base Year Market Size (2025) | USD 11.63 Billion |
| Market Size (2026) | USD 13.9 Billion |
| Market Size (2031) | USD 33.97 Billion |
| Growth Rate (2026 - 2031) | 19.55 % |
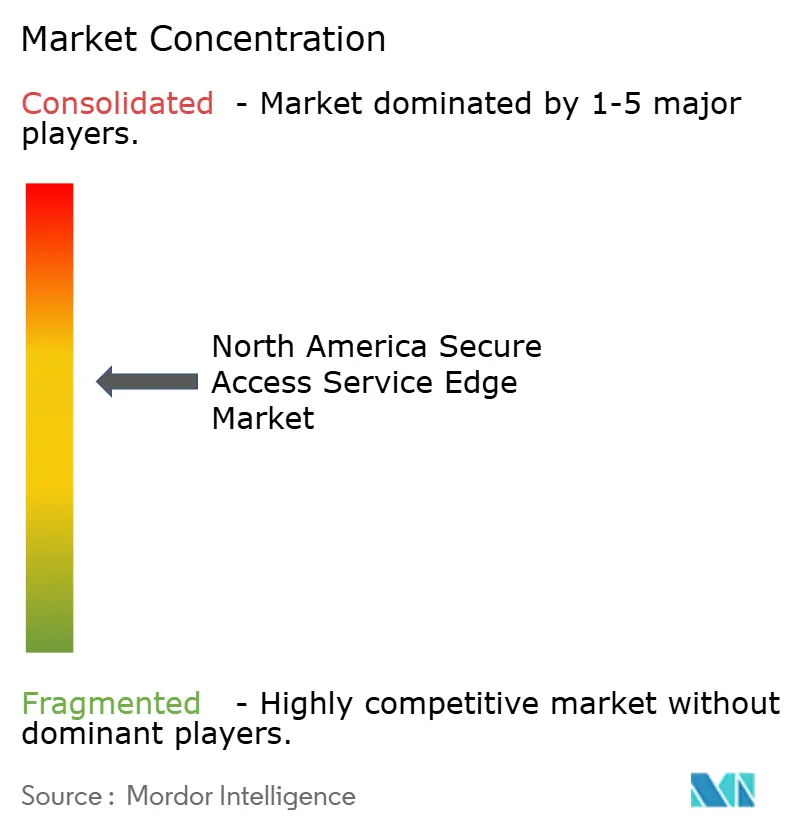
| Market Concentration | Medium |
Major Players *Disclaimer: Major Players sorted in no particular order Image ? 黑料不打烊. Reuse requires attribution under CC BY 4.0. | |
North America Secure Access Service Edge Market Analysis by 黑料不打烊
The secure access service edge market size in 2026 is estimated at USD 13.9 billion, growing from 2025 value of USD 11.63 billion with 2031 projections showing USD 33.97 billion, growing at 19.55% CAGR over 2026-2031. Rapid convergence of networking and security in a single cloud-native stack satisfies hybrid-work connectivity, suppresses recurrent cyber threats, and eliminates costly on-premise hardware. Cloud delivery removes geographic constraints, helping large enterprises standardize policy enforcement and allowing small and medium companies to acquire enterprise-grade protection without capital outlays. Persistent regulatory pressure around data privacy accelerates platform upgrades, while 5G-enabled edge connectivity fuels managed-service uptake among distributed branches. Leading vendors compete on AI-assisted orchestration that provisions dynamic policies, safeguards multi-cloud traffic, and trims operating expenses through automated troubleshooting.
Key Report Takeaways
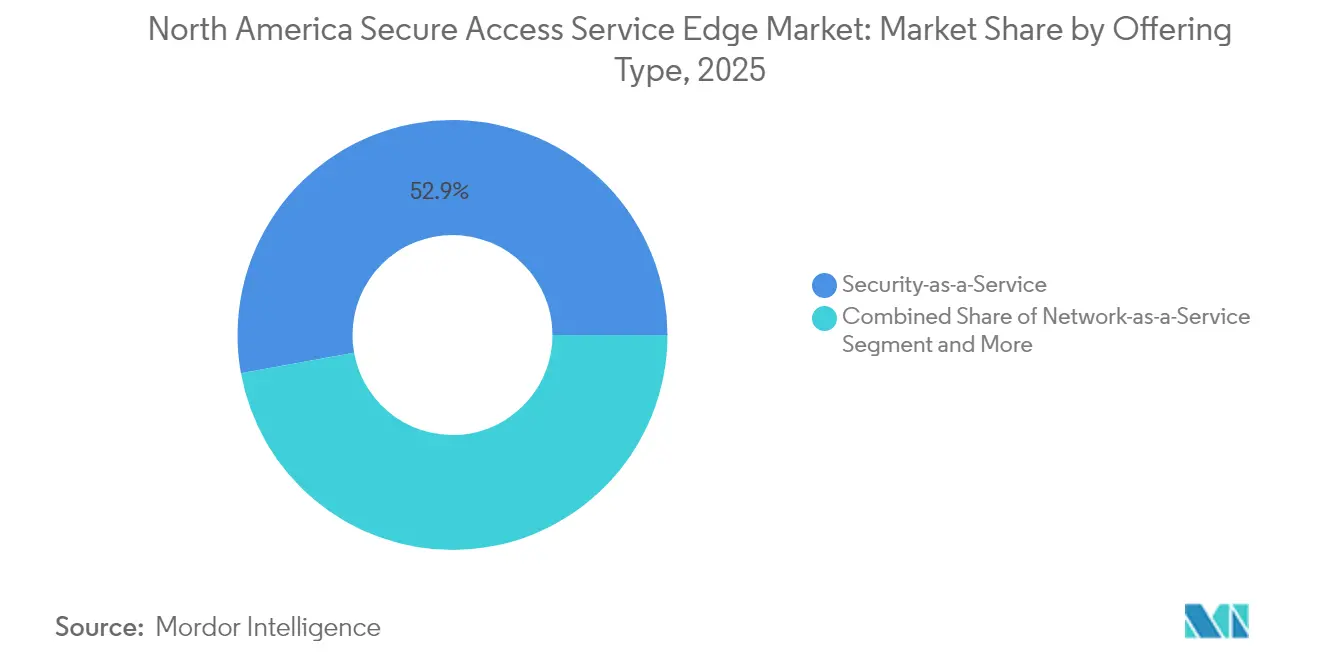
- By offering type, Security-as-a-Service captured 52.85% of secure access service edge market share in 2025, while Managed SASE Services is forecast to grow at 20.1% CAGR to 2031.
- By component, SD-WAN held 41.25% contribution to secure access service edge market size in 2025; Zero-Trust Network Access is poised to advance at 20.9% CAGR through 2031.
- By deployment mode, cloud deployments accounted for 64.92% of secure access service edge market size in 2025 and are expected to register 22.15% CAGR during the period.
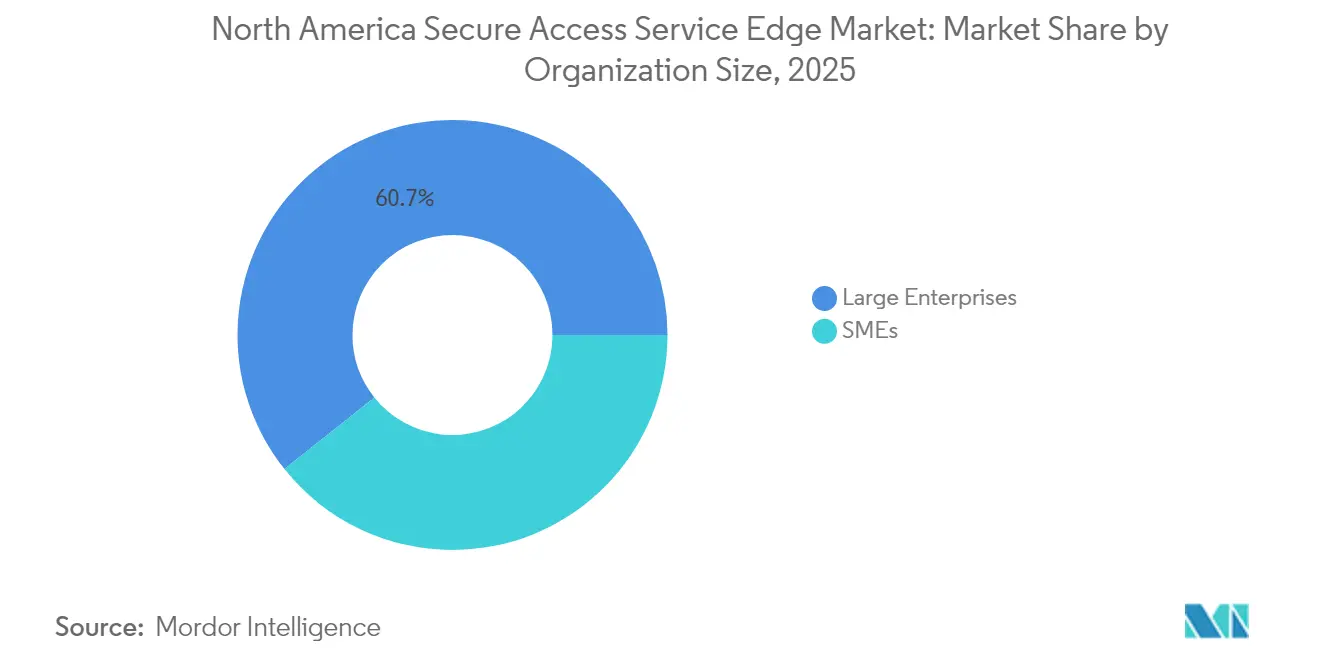
- By organization size, large enterprises controlled 60.72% of secure access service edge market size in 2025, whereas SMEs are expanding at 21.05% CAGR through 2031.
- By end-user vertical, BFSI commanded 27.05% revenue in 2025; healthcare is projected to grow at 19.95% CAGR through 2031.
- By country, the United States maintained 79.25% share of secure access service edge market size in 2025, while Mexico is anticipated to post 20.6% CAGR to 2031.
Note: Market size and forecast figures in this report are generated using 黑料不打烊’s proprietary estimation framework, updated with the latest available data and insights as of 2026.
North America Secure Access Service Edge Market Trends and Insights
Drivers Impact Analysis*
| Driver | (~) % Impact on CAGR Forecast | Geographic Relevance | Impact Timeline |
|---|---|---|---|
| Surge in hybrid-work connectivity demands | +4.2% | Global, with highest concentration in US and Canada | Short term (≤ 2 years) |
| Exploding multi-cloud and SaaS traffic volumes | +3.8% | North America core, spill-over to Mexico | Medium term (2-4 years) |
| Tightening data-privacy mandates (CCPA, Quebec Bill-64) | +2.9% | US California, Canada Quebec, expanding regionally | Long term (≥ 4 years) |
| AI-driven policy automation lowering OPEX | +3.1% | US enterprise hubs, Canada financial centers | Medium term (2-4 years) |
| 5G carriers bundling managed SASE at the edge | 2.7% | US major metros, Canada urban centers | Long term (≥ 4 years) |
| Sustainability push to consolidate branch hardware | 2.5% | North America, with early gains in tech corridors | Medium term (2-4 years) |
| Source: 黑料不打烊 | |||
Surge in Hybrid-Work Connectivity Demands
More than 80% of North American organizations plan Zero Trust adoption by 2026, reflecting a decisive shift away from legacy VPNs that reported an 82.5% increase in critical vulnerabilities between 2020 and 2025.[1]Mary Pratt, “Why 81% of Organizations Plan to Adopt Zero Trust by 2026,” CIO, cio.com SASE platforms enforce identity-centric access, micro-segmentation, and continuous verification, thereby stabilizing remote productivity. A case study from Salesforce recorded a fivefold bandwidth gain after swapping MPLS links for an SD-WAN-powered SASE backbone without inflating connectivity cost.
Exploding Multi-Cloud and SaaS Traffic Volumes
Direct cloud break-out via SD-WAN reduces round-trip latency up to five times compared with data-center backhaul, ensuring reliable SaaS performance.[2]Zeus Kerravala, “Achieving WAN Transformation with Security-Driven Networking,” Network World, networkworld.com SASE delivers uniform policy across Amazon Web Services, Microsoft Azure, and Google Cloud workloads. Cisco’s Cloud OnRamp cuts public-cloud onboarding from days to hours and optimizes routing for biopharma R&D platforms handling genome datasets.
Tightening Data-Privacy Mandates (CCPA, Quebec Bill-64)
California and Quebec privacy laws impose real-time breach notification and hefty penalties for data mismanagement. Native Data Loss Prevention inside SASE inspects traffic streams to block regulated content exfiltration. Healthcare illustrates urgency: 181 ransomware incidents exposed 25.6 million patient records in 2024, driving average ransom demands to USD 5.7 million.
AI-Driven Policy Automation Lowering OPEX
Cato Networks applies predictive analytics to recommend granular access rules that self-adjust as usage patterns shift, reducing manual ticket volumes. Palo Alto Networks adds natural-language prompts to its AI-Powered SASE so administrators can describe intent in everyday English rather than syntax-heavy commands.[3]Palo Alto Networks, “Salesforce Supercharges Its Bandwidth with Prisma SD-WAN,” paloaltonetworks.com
Restraints Impact Analysis*
| Restraint | (~) % Impact on CAGR Forecast | Geographic Relevance | Impact Timeline |
|---|---|---|---|
| Legacy MPLS migration complexity | -2.8% | US enterprise corridors, Canada financial districts | Medium term (2-4 years) |
| Cyber-security talent scarcity | -2.1% | North America, acute in rural and mid-tier cities | Long term (≥ 4 years) |
| Single-vendor lock-in concerns | -1.7% | US large enterprises, Canada government sectors | Short term (≤ 2 years) |
| Rural-broadband latency constraints | -1.4% | Rural US, remote Canada, northern Mexico | Long term (≥ 4 years) |
| Source: 黑料不打烊 | |||
Legacy MPLS Migration Complexity
MPLS bandwidth now grows only 6.7% through 2028, contrasted with cloud traffic that climbs 29% annually, leaving a widening performance gap. Rip-and-replace strategies risk downtime and mis-configured access controls, so many enterprises stage migration by overlaying SD-WAN tunnels on existing circuits. Temporary exposure of unused firewall rules can create lateral-movement opportunities that adversaries exploit during cut-over windows.
Cyber-Security Talent Scarcity
ISC? research reports that North America faces a shortfall of 500,000 qualified practitioners, with rural municipalities experiencing the steepest hiring challenges. Mexican executives mention talent deficits among the top three obstacles to 5G security adoption. SASE mitigates the gap by consolidating control planes and surfacing AI-generated recommendations that level workloads across lean IT teams.
*Our forecasts treat driver/restraint impacts as directional, not additive. The impact forecasts reflect baseline growth, mix effects, and variable interactions.
Segment Analysis
By Offering Type: Managed Services Accelerate Cloud Security Adoption
The secure access service edge market records Security-as-a-Service at 52.85% contribution in 2025 owing to preference for subscription models that eliminate capex. Managed SASE Services, though smaller today, shows a 20.1% CAGR and benefits from bundled connectivity that collapses firewall, VPN, and SD-WAN into a per-site fee. Telecom carriers deepen addressable reach by embedding clientless authentication in SIM cards, reducing provisioning friction for field workers. Professional Services remain critical during transition, guiding assessments, design validation, and post-migration optimization for highly regulated sectors such as banking. Network-as-a-Service reinforces subscription momentum through bandwidth-on-demand that scales during seasonal traffic peaks. Strategic alliances between integrators and hyperscalers further streamline adoption cycles as pre-tested reference architectures shorten proof-of-concept phases.
Service evolution also reflects vendor appetite to bolster recurring revenue. Verizon’s Advanced SASE, ATandT’s edge computing partnership, and T-Mobile’s 5G slices illustrate diversified roadmaps that broaden addressable verticals. Enterprises that once purchased security appliances every five years now renew cloud licenses annually, improving forecast accuracy for providers. As price competition intensifies, AI-enhanced self-service dashboards emerge as differentiation levers, empowering customers to tweak policies without professional-service engagements.


By Component: Zero Trust Reconfigures Network Foundations
SD-WAN furnished 41.25% revenue in 2025 and remains the baseline for traffic steering and dynamic path selection. Yet growth moderates as the technology becomes table-stakes. Zero-Trust Network Access rises on a 20.9% CAGR trajectory as remote access modernizes beyond VPN. Incorporation of device posture checks and user behavioral analytics reduces attack surface inside high-value workloads. Secure Web Gateway and Cloud Access Security Broker still attract compliance-driven spending among financial and healthcare entities that must log every SaaS transaction. Firewall-as-a-Service migrates distributed policy engines to cloud points of presence, cutting update latency. Data Loss Prevention gains from privacy mandates, while Digital Experience Monitoring helps operations teams diagnose latency spikes with real-time hop-by-hop visibility.
Component convergence favors single-vendor catalogs: Gartner forecasts that unified platforms will control 65% of SD-WAN procurement by 2027, up from 20% in 2024. Netskope’s purchase of Infiot produced a Borderless WAN delivering Zero Trust, quality-of-experience analytics, and application acceleration inside one portal. Fortinet integrates threat intelligence across next-generation firewall, SD-WAN, and secure edge, minimizing policy drift and expediting incident response.
By Deployment Mode: Cloud-First Outpaces On-Premise Holdings
Cloud accounts for 64.92% adoption and advances at 22.15% CAGR as enterprises dislodge data-center security stacks in favor of distributed inspection nodes closer to users. Scalability appeals to seasonal businesses that ramp capacity for promotional events then dial down to baseline. On-premise retains a foothold for low-latency trading desks and classified government workloads bound by sovereign mandates. Hybrid blueprints combine colocation gateways with SASE points of presence to maintain predictable performance while managing compliance. VMware’s portfolio exemplifies deployment flexibility by allowing customers to toggle between cloud gateways and locally hosted orchestrators without altering policy objects.
Edge computing reshapes the landscape further. 5G adoption climbs and pushes inspection to base-station proximity, cutting round-trip delay for augmented-reality maintenance in manufacturing plants. Carrier-controlled slices reserve predictable throughput and embed inline DNS filtering, closing gaps that previously existed between cellular and fixed branches. Energy-efficient hardware designed for remote office shelves supports the sustainability imperative to shrink rack density and power draw at subordinate sites.
By Organization Size: SMEs Narrow the Protection Gap
Large enterprises command 60.72% of revenue due to entrenched budget allocations and multicloud complexity that demands ultra-granular segmentation. Still, SMEs clock a 21.05% CAGR, capitalizing on pay-as-you-grow licensing that removes upfront hardware procurement. One cloud dashboard replaces a patchwork of disparate firewalls, content filters, and VPN concentrators, lowering training overhead. Technology partners target SMEs with pre-configured blueprints that auto-discover endpoints and push least-privileged rules in seconds.
For large organizations, consolidation motives dominate. Internal audits reveal overlapping firewall renewals, redundant web gateways, and scattered SSL decryption services that bloat opex. A pivot to a single platform achieves lower renewal complexity and simplifies vendor management. Governance gains as audit trails centralize under one management plane, satisfying board-level scrutiny on cyber-risk posture.
By End-User Vertical: Healthcare Surges as Threats Multiply
BFSI keeps 27.05% share due to strict regulatory frameworks such as PCI-DSS and FFIEC guidelines that direct continuous monitoring and data-in-motion encryption. Healthcare is the fastest riser at 19.95% CAGR as ransomware crews shift to double-extortion tactics, threatening to leak protected health information if payment stalls. Zero Trust Hospital architecture introduces micro-segmentation at every medical device, blocking lateral movement that often cripples radiology or infusion pumps during an attack. Retail benefits from omnichannel ordering, requiring branch connectivity that scales with seasonal peaks. Government agencies adopt the architecture to satisfy the U.S. Executive Order on Improving the Nation’s Cybersecurity, which stipulates a Zero Trust shift for federal networks. Manufacturing embraces SASE to guard operational technology that now stream telemetry directly to cloud analytics platforms.
Digital transformation aligns with pandemic-driven telehealth expansion. SASE integrates with HIPAA-compliant video solutions and EHR systems, performing in-line policy checks that ensure patient data remain confined to approved domains. Endpoint isolation restricts contractor access to specific hospital departments, preventing credentials hijacked from remote staff from pivoting into electronic records.
Geography Analysis
The secure access service edge market exhibits material regional divergence across North America. The United States contributes 79.25% revenue in 2025 thanks to dense enterprise clusters in Silicon Valley, New York, and Washington D.C. that require high-grade perimeterless security. Cloud migration across federal agencies and Fortune 500 banks sustains multiyear upgrades, reinforcing first-mover status. Tier-1 carriers partner with platform vendors to embed Zero Trust in 5G fixed-wireless offerings that backhaul traffic to nationwide SASE points of presence.
Canada follows with steady momentum anchored by Quebec Bill-64, which elevates data-sovereignty obligations and compels cross-border businesses to adopt uniform inspection across states and provinces. Financial centers in Toronto and Vancouver install cloud gateways that log flows in Canadian soil to satisfy local residency mandates. Healthcare networks adopt SASE to mitigate ransomware, leveraging AI analytics to flag anomalous East-West traffic within patient portals.
Regulatory Landscape
North American SASE adoption is tied to public-sector security architecture requirements and privacy obligations. In June 2026, the Cybersecurity and Infrastructure Security Agency (CISA) issued guidance that helps federal agencies transition from the Trusted Internet Connections (TIC) 2.0 model toward TIC 3.0 using SASE as part of broader Zero Trust implementation, reinforcing cloud-delivered inspection and policy enforcement patterns for government networks. Federal buyers also benchmark SASE implementations against the Federal Risk and Authorization Management Program (FedRAMP), which influences vendor authorization roadmaps and the documentation required for cloud security controls.
Cross-border data handling continues to shape regional SASE design decisions, especially around inspection, logging, and key management. The U.S. CLOUD Act (18 U.S.C. 2713) can compel service providers under U.S. jurisdiction to disclose data regardless of where it is stored. Separately, January 2026 guidance tied to the EU-U.S. Data Privacy Framework (DPF) emphasizes ongoing verification expectations for U.S. recipient certification status in cross-border transfers. Together, these pressures raise the weight of data residency choices, sub-processor governance, and audit-ready logging in purchase criteria across the United States, Canada, and Mexico.
Value Chain Analysis
In North America, the SASE value chain begins with cloud-native platform engineering across ZTNA, SWG, CASB, FWaaS, DLP, and SD-WAN control planes. It then extends to hyperscale and edge infrastructure that hosts points of presence, before reaching enterprise deployment and ongoing operations. Telecommunications carriers and managed service providers support a large share of orchestration by bundling connectivity with cloud security platforms and leveraging backbone reach, peering, and last-mile access to deliver consistent performance across distributed branches and mobile workforces. Partnerships such as AT&T working with Palo Alto Networks highlight how carrier networks and SASE stacks are integrated into enterprise-facing managed offers.
Downstream, value shifts to integration, migration, and governance services that connect identity providers, endpoint posture signals, and SIEM/SOAR telemetry into unified policy workflows. Public-sector and regulated-industry requirements add steps around authorization and evidence packaging, including alignment to FedRAMP expectations in federal procurements, along with operational controls for log retention and data residency. Interoperability mechanisms between security platforms and private network cores also matter for latency and performance, while supply-chain assurance increasingly includes mapping cloud sub-processors and managing decryption key sovereignty as traffic inspection moves from appliances into distributed cloud enforcement points.
Competitive Landscape
North American competition remains moderately consolidated. The top five vendors, led by Palo Alto Networks, Cisco, Zscaler, Fortinet, and Cato Networks, together oversee a sizable slice of recurring subscription revenue. Consolidation persists: Palo Alto Networks completed its USD 28 billion Splunk takeover in 2024, folding observability into security analytics to provide richer threat context. Cisco acquired IBM’s QRadar assets to infuse SIEM telemetry into Secure Connect, strengthening lateral-movement detection. Netskope added Infiot and now markets Borderless WAN that merges connectivity and security into one license.
Vendors differentiate on AI. Zscaler processes over 500 billion daily transactions through machine-learning models that correlate user, device, and destination risk scores. Cato’s Autonomous Policies predict optimal segmentation tags and auto-tune them to traffic shifts, easing administration for resource-constrained teams. Fortinet leverages custom ASICs inside its Security Fabric to push deep-packet inspection at wire rates that match high-speed fiber links, preserving user experience during cloud breakout.
North America Secure Access Service Edge Industry Leaders
Akamai Technologies Inc.
Aruba Networks (an HPE Company)
AT&T Inc.
Barracuda Networks Inc.
Broadcom Inc.
- *Disclaimer: Major Players sorted in no particular order

Market Opportunities and Future Outlook
Quantum-resilient networking and identity protection are starting to stand out as differentiated capability areas within SASE, particularly as enterprises seek upgrades for long-lived confidentiality and authentication flows. In July 2026, AT&T and Palo Alto Networks announced a quantum-resilient SASE fabric that integrates Prisma SD-WAN with AT&T network capabilities, framing post-quantum cryptography (PQC) as a practical upgrade path within managed SASE offerings. AT&T has also referenced the use of Cisco 8000 Series Secure Router capabilities for quantum-resilient encryption and authentication aligned to National Institute of Standards and Technology (NIST) standards. This points to an opportunity for vendors and carriers to package PQC-ready transport, certificate lifecycle controls, and crypto-agility into SASE contracts for critical infrastructure, BFSI, and government buyers.
Federal architecture modernization also creates a broader opportunity for providers that can operationalize compliance-grade telemetry and cloud security controls at scale. CISA guidance in June 2026, which supports agencies moving from TIC 2.0 to TIC 3.0 via SASE and includes expectations for feeding network telemetry to the Comprehensive Log Aggregation Warehouse (CLAW) cloud service, raises the bar for log pipelines, policy auditability, and managed operations. Alongside regional privacy constraints such as CCPA in California and Quebec Bill-64, and cross-border data-transfer scrutiny in the context of the Data Privacy Framework, buyers are prioritizing flexible deployment models, including cloud, VPC, or on-prem control options, plus data residency choices. That combination supports ongoing demand for platforms and managed services that can demonstrate governance across the United States, Canada, and Mexico.
Recent Industry Developments
- March 2026: Akamai Technologies Inc. announced AI-powered capabilities for Akamai Guardicore Segmentation, enabling AI-driven identification, analysis, and automatic policy generation for security enforcement. The launch expands SASE-like microsegmentation and zero-trust capabilities in the NA SASE market. Strengthens market position in AI-driven policy automation and dynamic segmentation across hybrid IT environments.
- August 2025: AT&T Inc. and Cisco delivered a comprehensive SASE solution enabling secure connectivity via Cisco Secure Access platform. The partnership gives a direct SASE deployment collaboration in NA market. The capacity addition strengthens consolidation of SASE offerings via single-vendor functionality, reducing operational complexity for enterprises.
- April 2025: Hewlett Packard Enterprise Aruba Networking expanded Aruba Central with virtual private cloud (VPC) and on-prem deployments to address data sovereignty and regional control. The capability enhances deployment flexibility and data-residency options for NA SASE customers. Broadens SASE adoption pathways through hybrid cloud/on-prem configurations.


Research Methodology Framework and Report Scope
Market Definition and Coverage
This market covers spending in North America on cloud-delivered secure access service edge offerings that combine network access and security controls for users, devices, and branch locations when connecting to applications and data.
Scope exclusions: We exclude customer-owned on-premise security appliances, pure MPLS transport services, and general IT outsourcing that is not sold as SASE functionality.
Segmentation Overview
- By Offering Type
- Network-as-a-Service
- Security-as-a-Service
- Managed SASE Services
- Professional Services (Assessment, Integration)
- By Component
- Software-defined WAN (SD-WAN)
- Secure Web Gateway (SWG)
- Cloud Access Security Broker (CASB)
- Zero-Trust Network Access (ZTNA)
- Firewall-as-a-Service (FWaaS)
- Data-Loss Prevention (DLP)
- Digital Experience Monitoring
- By Deployment Mode
- Cloud
- On-premise
- By Organization Size
- Large Enterprises
- SMEs
- By End-user Vertical
- Banking, Financial Services and Insurance (BFSI)
- IT and Telecommunications
- Retail and eCommerce
- Healthcare and Life Sciences
- Government and Public Sector
- Manufacturing and Industrial
- Education
- Other Industries
- By Country
- United States
- Canada
- Mexico
Data Sources, Market Sizing, and Validation
Desk Research
Desk research was used to set market boundaries, build the demand context, and keep assumptions tied to adoption signals seen in the North America market for SASE. We rely on public and official references such as NIST guidance and publications, FCC broadband and connectivity statistics, US SEC filings, and US government cyber reporting portals such as CISA, along with standards and best-practice material from ISO or similar bodies.
To translate market behavior into measurable inputs, we also reviewed cloud and network traffic commentary in annual reports, public documentation for product pricing cues, and procurement language from public tenders where accessible. In addition, paid subscriptions for company financials and intelligence, news and financials, patent databases, and global contracts and tenders were used to cross-check revenue exposure and timing of product rollouts. The desk research sources named here are illustrative only, and other references were used to collect data, validate assumptions, and clarify open questions during the analysis.
Primary Interviews and Surveys
Primary work focused on validating how enterprises in the US and Canada buy SASE, what they bundle together, and how pricing moves across contract lengths and user counts. We spoke with buyers, channel partners and managed service participants, and subject experts covering regulated industries and distributed enterprises. We then used the feedback to confirm adoption pace, discounting patterns, and the split between new deployments and renewals across North America.
Distribution of primary research fieldwork respondents
| Company type | Respondent position |
|---|---|
| Top tier: 39% | CXOs: 19% |
| Mid tier: 42% | Functional/Unit leaders: 33% |
| Smaller Players: 19% | Managers: 48% |
Market-Sizing & Forecasting
Sizing starts with a top-down build where enterprise network and security spend pools are reconstructed into a SASE demand set using adoption and attach rates for cloud-delivered secure access, followed by adjustments for subscription delivery and contract duration. We then corroborate totals with selective bottom-up checks, mainly sampled price per user or site multiplied by estimated deployed users or locations, plus supplier and channel sense-checks to avoid over-counting bundles.
Inputs were kept practical and traceable, including remote and hybrid workforce penetration, number of distributed sites, shift from VPN to zero-trust access, share of traffic inspected in cloud points of presence, and subscription pricing movement (including discounting and multi-year uplifts). Where direct volume is not visible, we fill gaps using proxy indicators such as public sector buying language, security compliance pressure, and renewal cycles reported by participants, then normalize the results across the region.
For forecasting, we run scenario analysis around upgrade cycles, cloud migration pace, and security incident pressure. The final path is refined using expert views on price progression and bundling changes. Assumptions are rechecked to ensure growth does not exceed feasible deployment capacity and customer budget ranges.
Data Validation & Update Cycle
Results are validated through triangulation across independent signals, then reviewed for abnormal jumps by year, country, and buyer type before sign-off. We also run variance checks against related cloud security and enterprise networking spending patterns, and we re-contact sources when a major assumption moves outside expected ranges.
Reports refresh annually, and interim updates are made when material events occur such as pricing resets, major policy shifts, or large contract announcements that can change run-rate. Before delivery, an analyst performs a fresh pass on key inputs and exchange-rate timing so clients receive the most current view available.
黑料不打烊's North America Secure Access Service Edge Market Size Compared Against Other Published Estimates
Published figures for North America SASE do not always match because the boundary between pure SASE subscriptions and adjacent networking or security services is drawn differently, and vendors package features in ways that blur what is being counted. Differences also show up when one publisher reports a contracted run-rate view while another uses recognized revenue, which shifts the year that growth appears.
Key gap drivers usually include how subscription pricing is normalized (per user versus per site), whether managed services and bundling are counted inside the same number, and how currency timing is handled when reporting across the US and Canada. When pricing and discount assumptions are refreshed on a set cadence and cross-checked against renewal behavior and procurement signals, 黑料不打烊 keeps the base-year market value closer to typical contract reality.
Benchmark comparison
| Source | Market Size | Gaps in Research Methodology |
|---|---|---|
| 黑料不打烊 | USD 11.63 B (2025) | |
| Regional Consultancy A | USD 9.80 B (2025) | Often restricts scope to security service edge subscriptions only, which can leave out SD-WAN-led SASE bundles used by distributed enterprises and reduce the implied subscription base. |
| Trade Journal B | USD 14.20 B (2025) | Commonly applies faster ASP uplift and counts a wider set of managed services and implementation fees inside the market, and may lean on run-rate extrapolations that pull forward renewals into the same year. |
The comparison suggests the spread is mainly explained by what gets included in subscription bundles and how pricing is rolled forward between years. When scope is kept to cloud-delivered SASE functions and pricing is normalized to typical contract structures, the resulting market size stays easier to reconcile with deployment cycles and procurement timing.


Key Questions Answered in the Report
What is the current value of the North American secure access service edge market?
The secure access service edge market size stands at USD 13.9 billion in 2026.
How fast is the market expected to grow?
The market is projected to post a 19.55% CAGR and reach USD 33.97 billion by 2031.
Which deployment model leads adoption?
Cloud deployment holds 64.92% share and is growing at 22.15% CAGR, reflecting strong preference for cloud-first security.
What vertical will grow the fastest?
Healthcare is projected to expand at 19.95% CAGR as hospitals combat ransomware and comply with privacy regulations.
Page last updated on:



